These days, everything is digital. We deal with data every day: from personal photos to work files that hold a lot of value. What happens if you lose that? Well, this is the reason behind doing secure backups of data. Let’s go through some best practices to keep your data safe and secure.
What is Data Backup?
Data backup refers to the creation of a copy of your data. The copy can be used in the event of loss or destruction of the original data. Backups can be stored on various devices, such as external hard drives, or in the cloud. Having a backup ensures you don’t lose important information.
Why is Secure Backup Important?
Backing up will save your data from being lost forever. Sometimes computers crash or get viruses. Other times, you may delete some important files accidentally. If you do not have a backup, then you could lose everything. Backing up your data keeps it safe from these problems.
How Often Should You Back Up Your Data?
Backing up your data is very important and should be done regularly. Some people back up their data every day, while others do it on a weekly basis. It depends on how often your data changes. If you have important files that change daily, then you should back them up every day. Regular backups mean you will always have the latest version of your files.
What Are the Different Types of Backups?
There are several types of backups you can use:
Full Backup
A full backup copies all your data. It takes more time and space but is very thorough.
Incremental Backup
An incremental backup only copies new or changed files since the last backup. It saves time and space.
Differential Backup
A differential backup copies all changes made since the last full backup. It’s faster than a full backup but takes more space than an incremental one.
Where to Store Your Backups
The place of storage for your backups is an important consideration:
External Hard Drives
These are physical devices you can store at home or at work. It’s convenient, but they can get lost or damaged.
Cloud Storage
It keeps your backups online, so it is safe from any form of physical damage. It’s also easily accessible from any location.
Offsite Storage
Offsite storage means keeping backups in a different location than your main data. This protects against theft or natural disasters.
How Can You Ensure Your Backups Are Secure?
Keeping your backups secure is as important as making them:
Use Encryption
Encryption scrambles your data so only you can read it. This keeps it safe from hackers.
Set Strong Passwords
Use strong passwords for all your backup accounts and devices. This prevents unauthorized access.
Regularly Test Your Backups
Testing ensures that your backups work properly. Try restoring a file to make sure everything is correct.
What Tools Can Help With Data Backup?
Many tools can help automate and manage backups:
Backup Software
Backup software can schedule and perform backups automatically. This makes it easier to keep up with regular backups.
Cloud Services
Many cloud services include automatic backups in their package. They provide extra security features too.
What Should You Avoid In Data Backup?
Here are some of the common mistakes to avoid while backing up your data:
Not Having Multiple Copies
Always have more than one copy of your backup in different places.
Ignoring Security Updates
Keep all backup software and devices updated to protect against new threats.
How Can You Make A Backup Plan?
Creating a backup plan helps you get organized by:
Determining what data should be backed up.
Frequency of backups.
Where the backups will be located.
Reminders to test regularly.
Take Action To Protect Your Data Today!
Don’t wait until it’s too late to protect your data. Start backing up today! Secure your important files by following these best practices for data backup. If you need help setting up a secure backup system, contact us today!
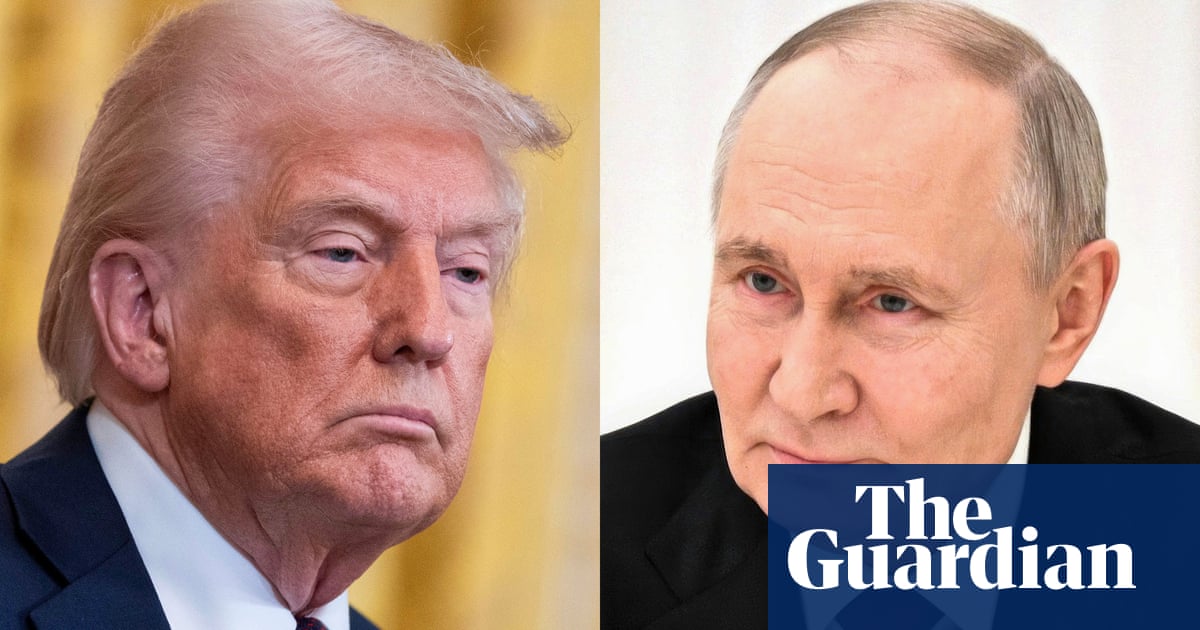
The Trump administration's response to Russian cyber threats: a retreat in strategy
The Trump administration has publicly and privately signaled that it does not believe Russia represents a cyber threat against US national security or critical infrastructure, marking a radical departure from longstanding intelligence assessments.
The shift in policy could make the US vulnerable to hacking attacks by Russia, experts warned, and appeared to reflect the warming of relations between Donald Trump and Russia’s president, Vladimir Putin.
Two recent incidents indicate the US is no longer characterizing Russia as a cyber security threat.
Liesyl Franz, deputy assistant secretary for international cybersecurity at the state department, said in a speech last week before a United Nations working group on cyber security that the US was concerned by threats perpetrated by some states but only named China and Iran, with no mention of Russia in her remarks. Franz also did not mention the Russia-based LockBit ransomware group, which the US has previously said is the most prolific ransomware group in the world and has been called out in UN forums in the past. The treasury last year said LockBit operates on a ransomeware-as-service model, in which the group licenses its ransomware software to criminals in exchange for a portion of the paid ransoms.
In contrast to Franz’s statement, representatives for US allies in the European Union and the UK focused their remarks on the threat posed by Moscow, with the UK pointing out that Russia was using offensive and malicious cyber attacks against Ukraine alongside its illegal invasion.
“It’s incomprehensible to give a speech about threats in cyberspace and not mention Russia and it’s delusional to think this will turn Russia and the FSB (the Russian security agency) into our friends,” said James Lewis, a veteran cyber expert formerly of the Center for Strategic and International Studies think tank in Washington. “They hate the US and are still mad about losing the cold war. Pretending otherwise won’t change this.”
The US policy change has also been established behind closed doors.
A recent memo at the Cybersecurity and Infrastructure Security Agency (Cisa) set out new priorities for the agency, which is part of the Department of Homeland Security and monitors cyber threats against US critical infrastructure. The new directive set out priorities that included China and protecting local systems. It did not mention Russia.
A person familiar with the matter who spoke to the Guardian on the condition of anonymity said analysts at the agency were verbally informed that they were not to follow or report on Russian threats, even though this had previously been a main focus for the agency.
The person said work that was being done on something “Russia-related” was in effect “nixed”.
“Russia and China are ourbiggest adversaries. With all the cuts being made to different agencies, a lot of cyber security personnel have been fired. Our systems are not going to be protected and our adversaries know this,” the person said.
The person added: “People are saying Russia is winning. Putin is on the inside now.”
The New York Times has separately reported that the Trump administration has also reassigned officials at Cisa who were focused on safeguarding elections from cyberattacks and other attempts to disrupt voting.
Another person who previously worked on US Joint Task Forces operating at elevated classification levels to track and combat Russian cyber threats said the development was “truly shocking”.
“There are thousands of US government employees and military working daily on the massive threat Russia poses as possibly the most significant nation state threat actor. Not to diminish the significance of China, Iran, or North Korea, but Russia is at least on par with China as the most significant cyber threat,” the person said.
The person added:“There are dozens of discrete Russia state-sponsored hacker teams dedicated to either producing damage to US government, infrastructure, and commercial interests or conducting information theft with a key goal of maintaining persistent access to computer systems.”
Cisa and the State Department did not respond to the Guardian’s requests for comment.
The change is not entirely surprising, given that the Trump administration has made it clear that it is seeking to make amends with Moscow. Earlier this week at the United Nations, the US voted with Russia against an EU-Ukrainian resolution that condemned Russia on the third anniversary of Russia’s invasion of Ukraine.
“The US has long assessed Russia, China and Iran as leaders in cyberthreats. To see a US representative in an international setting erase Russia’s role altogether comes as a bit of a shock – though consistent with the sudden US alignment with Russia and its satellites on the global stage,” said Scott Horton, an American lawyer who previously worked in Moscow and advised Russian human rights advocates.
The US has long warned that Russia posed a cyber threat to US infrastructure, including in the annual threat assessment published by US intelligence agencies last year. The report stated that Russia posed an “enduring global cyber threat” even as it has prioritized cyber operations against Ukraine. Moscow, the report concluded, “views cyber disruptions as a foreign policy lever to shape other countries’ decisions and continuously refines and employs its espionage, influence and attack capabilities against a variety of targets”. Russia was able to target critical infrastructure, industrial control systems, in the US and in allied and partner countries.
Few lawmakers have previously been as outspoken on the issue as Marco Rubio when he was still a Florida senator. In 2020, as chairman of the Senate intelligence committee, Rubio – who now serves as Trump’s secretary of state – said the US would retaliate for a massive and ongoing cyberattack that had compromised companies and federal agencies, including the energy department’s National Nuclear Security Administration. At the time he said the attacks were “consistent with Russian cyber operations”.
But there was no sign of that kind of rebuke from Franz, who now reports to Rubio at the state department. The change in language at the recent UN speech was not only remarkable for omitting Russia and LockBit, said Valentin Weber, senior research fellow at the German Council on Foreign Relations, but also for leaving out any mention of allies and partners.
“For a quarter century Putin’s Russia pushed an autocratic agenda in the UN cybersecurity negotiations, while engaging in nonstop cyberattacks and information operations around the world, and the US and other democracies pushed back,” said William Drake, director of international studies at the Columbia Institute for Tele-Information in Columbia Business School. “But now the Trump administration has abandoned the liberal international order… [and] the US is no longer a global power trying to maintain an open and rules-based international system, it’s just a great power with narrower self-interests that happen to be impacted by China’s cyberattacks.”
Do you have a tip on this story? Please message us on Signal at +1 646 886 8761
The Trump administration has recently indicated that it does not view Russia as a cyber threat to US national security or critical infrastructure, a departure from previous intelligence assessments. This shift in policy has raised concerns among experts about the potential vulnerability of the US to hacking attacks by Russia. The warming relations between President Donald Trump and Russian President Vladimir Putin seem to be influencing this change in stance.
Recent incidents have highlighted the US no longer characterizing Russia as a cyber security threat. Liesyl Franz, deputy assistant secretary for international cybersecurity at the state department, omitted any mention of Russia in her recent speech at a United Nations working group on cyber security, focusing instead on threats from China and Iran. This is in contrast to representatives from US allies in the European Union and the UK, who emphasized the threat posed by Moscow.
Behind closed doors, a memo at the Cybersecurity and Infrastructure Security Agency (Cisa) outlined new priorities that did not include Russia as a cyber threat. Analysts at the agency were reportedly instructed not to follow or report on Russian threats, despite it being a main focus previously.
The Trump administration's realignment with Russia has also been evident in other areas, such as voting with Russia against an EU-Ukrainian resolution condemning Russia's invasion of Ukraine. This shift in policy has surprised many, given Russia's history of cyber threats against US infrastructure and critical systems.
Despite warnings from US intelligence agencies about Russia's cyber capabilities, the Trump administration's change in stance on Russia as a cyber threat has raised concerns about the country's cybersecurity posture. Lawmakers like Marco Rubio have previously been vocal about the threat posed by Russia in cyberspace, but recent developments suggest a shift in US policy towards Russia.
Overall, the change in language and policy towards Russia in cybersecurity matters has raised questions about the US's approach to global cyber threats and its commitment to maintaining a rules-based international system. The impact of this shift remains to be seen, but experts warn that downplaying the threat posed by Russia could leave the US vulnerable to cyberattacks.
Understanding the Relationship Between Risk and Cybersecurity for Stronger Protection
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a Critical National Infrastructure (CNI). As such, cybersecurity is of utmost importance at the company, with Matt Webb serving as the CIO responsible for ensuring a robust cybersecurity posture.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in cybersecurity. To address this vulnerability, UKPN conducts phishing test campaigns and provides mandatory training to employees. Webb aims to make cybersecurity more meaningful for individuals at all levels of the organization by sharing real-world use cases and illustrating the potential consequences of cyber threats.
In addition to focusing on employee awareness and training, UKPN adheres to a comprehensive cyber assurance framework covering risk management, protection, detection, and mitigation. The company is also working towards achieving an enhanced cybersecurity profile by the end of 2027, in response to increasing cybersecurity threats and regulatory requirements.
By emphasizing the human aspect of cybersecurity and sharing relevant use cases, UKPN aims to create a culture of cybersecurity awareness and diligence throughout the organization. Webb believes that making cybersecurity more relatable and tangible to individuals will ultimately strengthen the company's overall cybersecurity resilience.
Understanding the Importance of Relating Risk to Robust Cybersecurity
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a Critical National Infrastructure (CNI). As such, cybersecurity is of utmost importance at the company, with Matt Webb, UKPN CIO, leading the charge.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in cybersecurity. To address this, UKPN conducts phishing test campaigns and provides mandatory training to employees who fail. Webb aims to make cybersecurity more meaningful to individuals by sharing real-world use cases and illustrating the potential consequences of cyber threats.
UKPN adheres to a robust cyber assurance framework that covers areas such as risk management, protection, detection, and mitigation. Regulatory standards are constantly evolving, with OFGEM driving the need for enhanced cybersecurity resilience. UKPN aims to achieve this enhanced profile well before the regulatory target of 2027.
Webb emphasizes the importance of making cybersecurity exercises feel real and impactful, especially for the executive team. By sharing examples of the potential impact of cyber threats and conducting tests with real-world scenarios, UKPN aims to inspire greater diligence and awareness of cybersecurity at all levels of the organization.
Understanding the Relationship Between Risk and Cybersecurity to Enhance Protection
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a part of the Critical National Infrastructure (CNI). As a designated CNI, any disruption to UKPN's services could have widespread effects on other aspects of CNI. This is why cybersecurity is of utmost importance at the company, with Matt Webb, UKPN CIO, being ultimately responsible for it.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in cybersecurity. To address this vulnerability, UKPN conducts phishing test campaigns and provides mandatory training to employees who fail. The goal is to make cybersecurity meaningful for individuals at all levels of the organization by sharing real-world use cases and illustrating the potential consequences of cyber threats.
In addition to focusing on employee awareness and training, UKPN also adheres to a robust cyber assurance framework that covers areas such as risk management, protection, detection, and mitigation. The company is working towards achieving an enhanced cybersecurity profile by the end of 2027, ahead of regulatory requirements.
By making cybersecurity relevant and tangible to individuals within the organization, UKPN aims to create a culture of cybersecurity awareness and diligence. This includes targeting every level of the organization, including the executive team, and conducting real-world test exercises to simulate cyber threats and their potential impact. Ultimately, UKPN's approach to cybersecurity aims to keep the lights on and protect critical infrastructure from cyber threats.
Understanding the Importance of Relating Risk to Robust Cybersecurity
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a Critical National Infrastructure (CNI). As such, cybersecurity is of utmost importance at the company, with Matt Webb, UKPN CIO, ultimately responsible for ensuring a robust cybersecurity posture.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in security. To address this, UKPN conducts sustained phishing test campaigns and provides mandatory training to employees who fail. The goal is to make cybersecurity meaningful for individuals at all levels of the organization by sharing real-world use cases and illustrating the potential consequences of cyber threats.
In addition to focusing on employee awareness and training, UKPN adheres to a comprehensive cyber assurance framework that covers areas such as risk management, protection, detection, and mitigation. Regulatory standards are also evolving, with regulators like OFGEM driving the need for enhanced cybersecurity resilience across all facets of cyber.
While the regulatory target for achieving an enhanced cybersecurity profile is the end of 2027, UKPN is working to accelerate this process and achieve the top level of resilience as soon as possible. By engaging employees at all levels of the organization and emphasizing the real-world impact of cybersecurity threats, UKPN aims to create a culture of cybersecurity awareness and diligence throughout the company.
Understanding the Relationship Between Risk and Cybersecurity for Enhanced Protection
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a part of the Critical National Infrastructure (CNI). As such, cybersecurity is of utmost importance at the company, with Matt Webb serving as the CIO responsible for ensuring a robust cybersecurity posture.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in cybersecurity. To address this, UKPN conducts sustained phishing test campaigns and provides mandatory training to employees who fail the tests. The company aims to make cybersecurity meaningful for individuals at all levels of the organization by sharing real-world use cases and examples of cyber threats.
In addition to focusing on awareness and training, UKPN also adheres to a comprehensive cyber assurance framework covering risk management, protection, detection, and mitigation. The company is working towards achieving an enhanced cybersecurity profile by the end of 2027, ahead of regulatory requirements.
By making cybersecurity relevant and tangible for employees, UKPN aims to create a culture of cyber resilience and vigilance throughout the organization. Webb emphasizes the importance of engaging all levels of the organization, including the executive team, in cybersecurity testing exercises to ensure preparedness for real-world cyber threats.
Understanding the Relationship Between Risk and Cybersecurity for Enhanced Protection
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a Critical National Infrastructure (CNI). As such, cybersecurity is of utmost importance at the company, with Matt Webb serving as the CIO responsible for ensuring a robust cybersecurity posture.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in cybersecurity. To address this, UKPN conducts sustained phishing test campaigns and provides mandatory training to employees who fail. The company aims to make cybersecurity more meaningful for individuals at all levels of the organization by sharing real-world use cases and examples of cyber threats.
In addition to focusing on employee awareness and training, UKPN adheres to a robust cyber assurance framework that covers areas such as risk management, protection, detection, and mitigation. The company is working towards achieving an enhanced cybersecurity profile by the end of 2027, ahead of regulatory requirements.
Webb emphasizes the importance of making cybersecurity real and relevant to individuals within the organization, including the executive team. By sharing examples of the impact of cyber threats and conducting real-world test exercises, UKPN aims to inspire greater diligence and awareness when it comes to cybersecurity.
Understanding the Relationship Between Risk and Cybersecurity for Enhanced Protection
UKPN keeps the lights on by making cybersecurity meaningful for individuals at all levels of the business
Image:
How to avoid this scenario for robust cybersecurity?
A robust cybersecurity posture is about more than technology and frameworks but companies often struggle to convey why it matters. Matt Webb, UKPN CIO explains why he takes a human first approach to cyber.
Critical National Infrastructure (CNI) refers to the essential systems, assets and services that a country depends on to function. UK Power Networks (UKPN) is designated CNI due to its role of distributing electricity across London, the Southeast, and East of England. A disruption to UKPN’s services could lead to widespread power outages, with all the knock-on effects on other aspects of CNI.
Cybersecurity is of the utmost importance at the company and Matt Webb, UKPN CIO is ultimately answerable for it.
“It's a big function,” Webb acknowledges, “but there is value in having those technology-oriented functions together.” The alternative structure is cybersecurity reporting into the risk management line but Webb argues that at UKPN this simply wouldn’t be effective.”
Image
Description
Matt Webb, UKPN
“When you look at what the cyber assurance framework entails, it cuts across all facets of IT as you expect. To have it as a separate body, imposing change on those that are doing it would increase complexity so having us all within the one tent allows us to have much better cohesion and hopefully a better result.”
The cyber assurance framework Webb refers to is a cybersecurity framework that UKPN adheres to. It’s a robust framework covering areas such as managing risk, protection, detection and mitigation. Nonetheless, given the increasing bleakness of the geopolitical outlook, and the rising likelihood of more severe cyberattacks, regulators are raising the bar.
“It's a well-established cyber standard, but there are different levels of maturity,“ Webb says. “We have the level of accreditation that's currently required from a regulatory standpoint but OFGEM, because of the increasing cybersecurity threat, is driving the need to have an enhanced profile, which is the top level of resilience across all the different facets of cyber.”
The regulatory target is to have this enhanced profile by the end of 2027, but Webb isn’t planning on hanging around.
“We're not waiting to tick that box in 2027 we're looking to accelerate that and achieve that level as soon as possible. There are certain areas where we're more mature and already enhanced profile, and others where we're on that development pathway. Each DNO [Distribution Network Operator – there are 14 in total across the UK] is going through the same process.”
Keeping it real
Webb understands that cybersecurity is a very people-oriented discipline – or at least, it should be. However, the cybersecurity industry hasn’t always helped itself by making sneering allusions to people being ‘the weakest link.’ Webb frames the challenge with considerably more diplomacy.
“You can have the best technology in the world, but it’s the squidgy human that poses the greatest vulnerability in most instances. The behavioural, cultural and awareness aspects of cyber are part of the cyber resilience program of work as well as being delivered under BAU [Business as Usual].
“For instance, we have sustained phishing test campaigns where we put out spoof phishing emails and follow up with mandatory training if they fail. What we are beginning to do more of is trying to bring it to life and make it more meaningful to individuals. Everyone knows about cyber security. You can't turn on the TV for five minutes and there not be something to do with cyber so the awareness is there. But we need people to ask ‘what does it mean to me? What role do I play? Why should I care?’ That’s where I think there’s a gap.”
Part of Webb’s strategy is to bridge this gap by sharing pertinent use cases which occur in the real world and illustrate real world consequences. This adds context and colour to the concept of cybersecurity which can often appear to individuals as abstract or esoteric. He continues:
“A good example of that is the increasing instance of AI enabled deepfake images or videos to extort payments. That’s not what most people think about when you talk about cyber security. An example I gave recently where a CFO authorized a payment off the back of a deep fake Teams interaction. We share use cases that make it a bit more real.
“Equally, we target every level of the organisation including our executive team. There's always a challenge in making these test exercises feel real. The goal is stopping them being purely academic exercises and to test things in anger with real world concepts and scenarios and by sharing examples of the impact.
“For instance, one of the things we did with the last round of testing was to ask an independent party to scan the Internet to understand what we could find in terms of publicly available information about our executive team. We then put that in front of them and asked if they were aware of it. It’s about how you make it real, and that's one that might change behaviours and inspire a little bit more diligence when it comes to cybersecurity.”
UK Power Networks (UKPN) plays a crucial role in distributing electricity across London, the Southeast, and East of England, making it a Critical National Infrastructure (CNI). As such, cybersecurity is of utmost importance to the company, with Matt Webb serving as the CIO responsible for ensuring a robust cybersecurity posture.
Webb takes a human-first approach to cybersecurity, recognizing that people are often the weakest link in cybersecurity. To address this vulnerability, UKPN conducts sustained phishing test campaigns and provides mandatory training to employees who fail. The goal is to make cybersecurity meaningful to individuals at all levels of the organization by sharing real-world use cases and illustrating the potential consequences of cyber threats.
In addition to focusing on employee awareness and training, UKPN adheres to a comprehensive cyber assurance framework that covers areas such as risk management, protection, detection, and mitigation. Regulatory standards are also evolving to address the increasing cybersecurity threat, with OFGEM driving the need for enhanced resilience across all facets of cyber.
While the regulatory target for achieving an enhanced cybersecurity profile is set for 2027, UKPN is actively working to accelerate this process and achieve the highest level of resilience as soon as possible. By engaging employees at all levels of the organization and emphasizing the real-world impact of cyber threats, UKPN aims to strengthen its cybersecurity posture and protect its critical infrastructure from potential cyberattacks.
Why Cybersecurity Concerns Everyone: Insights from Jamaica Observer
Cybersecurity is an ongoing challenge for organisations.
Dear Editor,
I attended the Ministry of National Security’s two-day Cybersecurity Expo at the AC Hotel Kingston on February 11-12, 2025. Here are my questions: What was the purpose of the conference? What did it achieve? Were the people who attended satisfied with the two days of events? What did they learn that they were not aware of before?
I listened keenly to the different speakers, who were good because they spoke in language that anyone could understand, whether you were familiar with cybersecurity or not. There were speakers telling us how safe their platforms were. I knew that already. There were speakers telling us about the legality of protecting us in cyberspace; speakers telling us about how fast they can identify a break-in; speakers telling us about the risk to national security, etc. But in reality, what did I really learn that I did not know before?
So here is what I learnt that I did not know before. I learnt that it took 200 days for some companies to recognise that there was an intruder in their system, and it took 70 days to correct the problem. I learnt that with Darktrace artificial intelligence (AI) this time could be cut down to seconds.
I listened to a representative from Symptai who gave a very interesting presentation on how to test a system. I hope the agencies were listening because, hear me well, you can boast about how effective your systems are until the cows come home, but if you don’t hack it, you won’t know if it will work. The reality is if you put up security around your property and don’t test it, how are you going to be sure it will work when you are under attack.
Cybersecurity is an ongoing, daily challenge.
I listened and also spoke to a few presenters and was pleasantly surprised that I was not way off in some of my thinking. One of the biggest challenges we are facing is a lack of understanding of what the reality is. As someone pointed out, cybersecurity is not just the IT Department’s or IT personnel’s responsibility, it is the responsibility of everyone in an organisation.
Let’s look at a situation in which an employee is at work and decides to open his/her personal e-mail and clicks on something in it. In doing so the employee unknowingly compromises the network. Do we know how easy it is to hack a system or introduce something into a system by just going into an office and having access to a computer and a USB portal? Do we understand? The powers who set up the bureaucracies, do you all understand that people spend hours trying to find a way into systems? That is their job.
How are we going to compete or stop them when it takes six months to a year to procure an item that is needed to fix the leak in a system? By the time you get permission to purchase the item or software, it changes and is now outdated. Meanwhile, the hacker is creating a new malware or worm or whatever they need to hit you again.
The other thing I learnt was secrecy is a great help to the hackers. Let us look at an example: Bank A gets hacked, it remains silent, hoping no one will find out. Bank B gets hacked a few days later, this information is leaked. You would think that Bank A would contact Bank B and have a conversation, right? Wrong. Bank A instead says: Our system is safe, come and bank with us, we have put everything in place to protect our customers.
Because companies do not share certain information with each other, the hacker continues to smile because not only is he hacking away happily, he is also dividing and conquering.
Companies need to share with each other how they were hacked, how long it took them to find out, how they plugged the hole, and what they have put in place to protect themselves. People, you all need to understand that sharing helps each company to get stronger. Therefore, if Bank A has a breach, do you think it is not going to affect Bank B? If you think it can’t, then you are battling a war that you don’t understand.
Small companies need help to acquire proper software and train their staff to be able to constantly monitor their systems.
We need skilled personnel; yes, skilled hackers who are fierce but have integrity. We still have some of those, not everybody has gone over to the Dark Web, there are still some on the Lord’s side. But here is the part companies don’t want to hear, you have to pay them well. You have to pay real wages if you want them to focus on protecting your system every second, every hour of every day, just like the ones on the other side who are doing it for money and the challenge.
Finally, I learnt that there are laws that will allow the Office of the Director of Public Prosecutions to make bites and not just bark. That’s good. We still have a long journey but this is a good start.
Cybersecurity is everybody’s business but not everybody has to be involved. What do I mean? Most people don’t have to know how the system is breached or what is done to fix it. But everyone must be cautious and willing to ask questions of organisations who have collected their data, whether it be government agencies or private companies. Do not take it for granted that it is being protected, ask questions and demand answers. When in doubt, protest.
Be wise when surfing the World Wide Web, which includes social media, getting hacked is easy, even when you have protection. When in doubt — do not click.
Shirley Nelson
nelsenbless@gmail.com
Cybersecurity remains a persistent challenge for organizations, requiring constant vigilance and proactive measures to protect sensitive data and systems. Recently, the Ministry of National Security hosted a Cybersecurity Expo in Kingston, where experts and attendees discussed the latest trends and strategies in cybersecurity.
One key takeaway from the event was the importance of understanding the timeline of cyber threats. It was revealed that some companies took up to 200 days to detect an intruder in their system, highlighting the need for faster response times. Technologies like Darktrace artificial intelligence (AI) were showcased as tools to reduce detection and response times to mere seconds.
Another crucial aspect emphasized at the expo was the necessity of testing cybersecurity systems regularly. Simply having security measures in place is not enough; organizations must actively test their defenses to ensure they are effective against potential threats. Additionally, it was highlighted that cybersecurity is not solely the responsibility of IT departments but requires a collective effort from all employees within an organization.
The event also shed light on the importance of information sharing among companies. By openly discussing cybersecurity breaches, response times, and preventative measures, organizations can collectively strengthen their defenses against cyber threats. Furthermore, the expo underscored the need for skilled cybersecurity professionals who are well-compensated for their expertise in protecting systems from malicious attacks.
Overall, the Cybersecurity Expo served as a reminder that cybersecurity is a shared responsibility that requires ongoing attention and collaboration. By staying informed, asking questions, and demanding transparency from organizations that handle sensitive data, individuals can play a role in safeguarding against cyber threats in an increasingly digital world.