What Is SaaS Ransomware & How Can You Defend Against It?

Software-as-a-Service (SaaS) has revolutionized the way businesses operate. It offers convenience, scalability, and efficiency. No more dragging software from one device to another. Everyone can collaborate easily in the cloud.

But alongside its benefits, SaaS brings with it potential threats. When software and data are online, they’re more vulnerable to attacks. One of the latest threats to move from endpoint devices to the cloud is ransomware.

Ransomware has been around attacking computers, servers, and mobile devices for a while. But recently there has been an alarming uptick in SaaS ransomware attacks.

Between March and May of 2023, SaaS attacks increased by over 300%. A study in 2022 by Odaseva found that 51% of ransomware attacks targeted SaaS data.

In this article, we’ll delve into what SaaS ransomware is and the risks it poses. And, most importantly, how you can defend against it.

What is SaaS Ransomware?

SaaS ransomware is also known as cloud ransomware. It’s malicious code designed to target cloud-based applications and services. These include services like Google Workspace, Microsoft 365, and other cloud collaboration platforms.

The attackers exploit vulnerabilities in these cloud-based systems. The ransomware then encrypts valuable data. It effectively locks users out of their own accounts. Cybercriminals hold the data hostage. They then demand a ransom, often in the form of cryptocurrencies. The ransom is in exchange for the decryption key.

The Risks of SaaS Ransomware

SaaS ransomware adds a new layer of complexity to the cybersecurity landscape. It presents several risks to individuals and organizations.

Defending Against SaaS Ransomware

As the saying goes, prevention is better than cure. When it comes to SaaS ransomware, proactive defense is key. Here are some effective strategies to protect your organization against these threats.

Educate Your Team

Start by educating your employees about the risks of SaaS ransomware. Include how it spreads through phishing emails, malicious links, or breached accounts. Teach them to recognize suspicious activities and report any unusual incidents immediately.

Enable Multi-Factor Authentication (MFA)

MFA is an essential layer of security. It requires users to provide an extra form of authentication to access accounts. This is often a one-time code sent to their mobile device. Enabling MFA reduces the risk of unauthorized access. This is true, even if a hacker compromises an account's login credentials.

Regular Backups

Frequently backing up your SaaS data is crucial. In the event of a ransomware attack, you still have your data. Having up-to-date backups ensures that you can restore your files. You won’t need to pay the attacker’s ransom demands.

Apply the Principle of Least Privilege

Limit user permissions to only the necessary functions. Follow the principle of least privilege. This means giving users the lowest privilege needed for their job. Doing this, you reduce the potential damage an attacker can do if they gain access.

Keep Software Up to Date

Ensure that you keep all software (SaaS applications, operating systems, etc.) up to date. They should have the latest security patches installed. Regular updates close known vulnerabilities and strengthen your defense.

Deploy Advanced Security Solutions

Consider using third-party security solutions that specialize in protecting SaaS environments. These solutions can provide many benefits. Including:

Track Account Activity

Put in place robust monitoring of user activity and network traffic. Suspicious behavior can be early indicators of an attack. One example to watch for is several failed login attempts. Another is access from unusual locations.

Develop an Incident Response Plan

Prepare and practice an incident response plan. It should outline the steps to take in the event of a ransomware attack. A well-coordinated response can mitigate the impact of an incident. It can also aid in faster recovery. The sooner your team can respond, the faster business gets back to normal.

Don’t Leave Your Cloud Data Unprotected!

SaaS ransomware is a significant cybersecurity concern. The best defense is a good offense. Do you need help putting one together?

Our team can help you stay ahead of the cyber threats that lurk in the digital world. Give us a call today to schedule a chat.

--
Featured Image Credit

This Article has been Republished with Permission from The Technology Press.

The U.S. Government Files Lawsuit Against SolarWinds for Fraud, Citing Alleged Neglect of Cyber Security Leading to Russian Hack on Justice and Homeland Security Departments

U.S. regulators on Monday sued SolarWinds, a Texas-based technology company whose software was breached in a massive 2020 Russian cyberespionage campaign, for fraud for failing to disclose security deficiencies ahead of the stunning hack.

The company’s top security executive was also named in the complaint filed by the Securities and Exchange Commission seeking unspecified civil penalties, reimbursement of “ill-gotten gains” and the executive’s removal.

Detected in December 2020, the SolarWinds hack penetrated U.S. government agencies including the Justice and Homeland Security departments, and more than 100 private companies and think tanks. It was a rude wake-up call that raised awareness in Washington about the urgency of stepping up efforts to better guard against intrusions.

In the 68-page complaint filed in New York federal court, the SEC says SolarWinds and its then vice president of security, Tim Brown, defrauded investors and customers “through misstatements, omissions and schemes” that concealed both the company’s “poor cybersecurity practices and its heightened — and increasing — cybersecurity risks.”

In a statement, SolarWinds called the SEC charges unfounded and said it is “deeply concerned this action will put our national security at risk.”

Brown performed his responsibilities “with diligence, integrity, and distinction,” his lawyer, Alec Koch, said in a statement. Koch added that “we look forward to defending his reputation and correcting the inaccuracies in the SEC’s complaint.” Brown’s current title at SolarWinds is chief information security officer.

The SEC’s enforcement division director, Gurbir S. Grewal, said in a statement that SolarWinds and Brown ignored “repeated red flags” for years, painting “a false picture of the company’s cyber controls environment, thereby depriving investors of accurate material information.”

The very month that SolarWinds registered for an initial public offering, October 2018, Brown wrote in an internal presentation that the company’s “current state of security leaves us in a very vulnerable state,” the complaint says.

Among the SEC’s damning allegations: An internal SolarWinds presentation shared that year said the company’s network was “not very secure,” meaning it was vulnerable to hacking that could lead to “major reputation and financial loss.” Throughout 2019 and 2020, the SEC alleged, multiple communications among SolarWinds employees, including Brown, “questioned the company’s ability to protect its critical assets from cyberattacks.”

SolarWinds, which is based in Austin, Texas, provides network-monitoring and other technical services to hundreds of thousands of organizations around the world, including most Fortune 500 companies and government agencies in North America, Europe, Asia and the Middle East.

The nearly two-year espionage campaign involved the infection of thousands of customers by seeding malware in the update channel of the company’s network management software. Capitalizing on the supply-chain hack, the Russian cyber operators then stealthily penetrated select targets including at least nine U.S. government agencies and prominent software and telecommunications providers.

In its statement, SolarWinds called the SEC action an “example of the agency’s overreach (that) should alarm all public companies and committed cybersecurity professionals across the country.”

It did not explain how the SEC’s action could put national security at risk, though some in the cybersecurity community have argued that holding corporate information security officers personally responsible for identified vulnerabilities could make them less diligent about uncovering and/or disclosing them — and discourage qualified people from aspiring to such positions.

Under the Biden administration, the SEC has been aggressive about holding publicly traded companies to account for cybersecurity lapses and failures to disclose vulnerabilities. In July, it adopted rules requiring them to disclose within four days all cybersecurity breaches that could affect their bottom lines. Delays would be permitted if immediate disclosure poses serious national-security or public-safety risks.

Victims of the SolarWinds hack whose Microsoft email accounts were violated included the New York federal prosecutors’ office, then-acting Homeland Security Secretary Chad Wolf and members of the department’s cybersecurity staff, whose jobs included hunting threats from foreign countries.

U.S. regulators have filed a lawsuit against SolarWinds, a Texas-based technology company, for fraud in connection with the 2020 Russian cyberespionage campaign. The breach, which targeted SolarWinds' software, affected numerous U.S. government agencies and private companies. The Securities and Exchange Commission (SEC) has named the company's top security executive, Tim Brown, in the complaint, seeking civil penalties, reimbursement of gains, and his removal from the company.

The SEC alleges that SolarWinds and Brown defrauded investors and customers by concealing the company's poor cybersecurity practices and increasing cybersecurity risks. The complaint states that the company ignored red flags and provided a false picture of its cyber controls environment, depriving investors of accurate information.

SolarWinds has responded to the charges, calling them unfounded and expressing concern about the impact on national security. Brown's lawyer has defended his reputation and plans to correct inaccuracies in the SEC's complaint.

The SolarWinds hack, detected in December 2020, penetrated U.S. government agencies such as the Justice and Homeland Security departments, as well as private companies and think tanks. This incident highlighted the need for increased efforts to protect against cyber intrusions.

The SEC's action against SolarWinds is part of a broader trend of holding publicly traded companies accountable for cybersecurity lapses. Under the Biden administration, the SEC has adopted rules requiring companies to disclose cybersecurity breaches promptly.

The SolarWinds hack involved infecting thousands of customers by planting malware in the company's network management software. Russian cyber operators then targeted select organizations, including U.S. government agencies and prominent software and telecommunications providers.

SolarWinds provides network-monitoring services to numerous organizations worldwide, including Fortune 500 companies and government agencies. The company's statement criticized the SEC's action as an example of overreach that could discourage cybersecurity professionals from taking on such positions.

The impact of the SEC's action on national security remains unclear, but concerns have been raised about the potential consequences of holding information security officers personally responsible for vulnerabilities.

Overall, the SEC's lawsuit against SolarWinds reflects the increasing focus on cybersecurity and the need for companies to prioritize robust security measures and transparent disclosure of vulnerabilities.

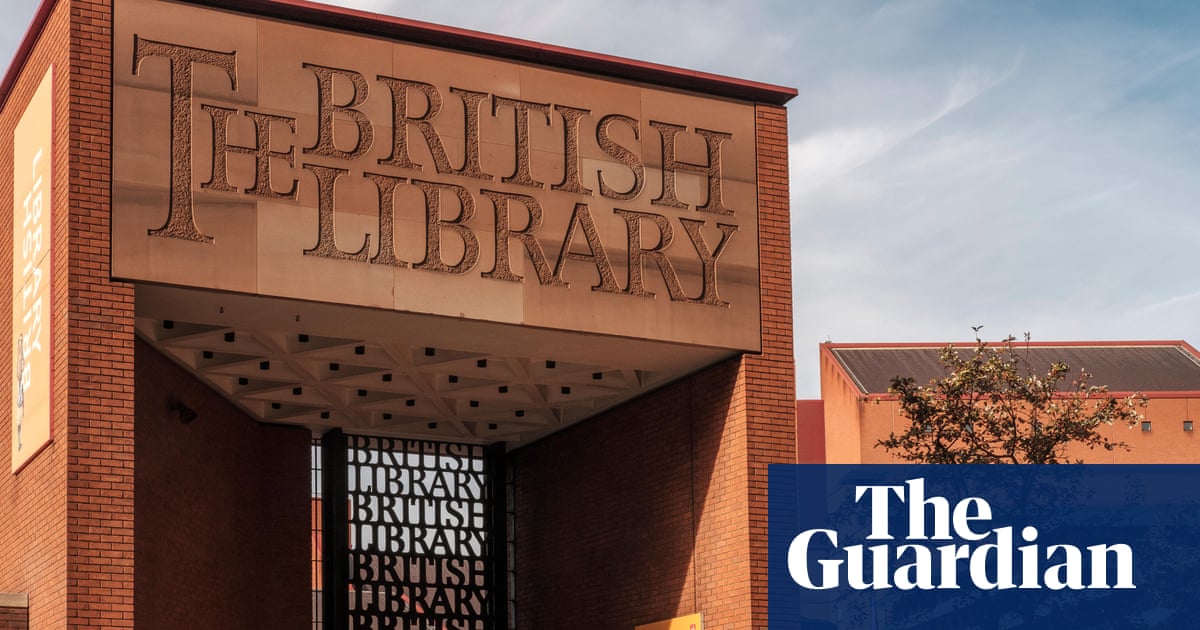
British Library experiences significant technology outage following cyber-attack

The British Library is suffering a technology outage after it was hit by a cyber-attack, which is affecting services online and its sites in London and Yorkshire.

Access to the website, as well as the catalogue and digital collections, is temporarily unavailable. The collection of items ordered on or after 27 October, new collection item orders via digital catalogues and reading room PCs are also inaccessible, it said. Reader registration is also unavailable.

The British Library said on Tuesday it had launched an investigation into the incident with the support of the National Cyber Security Centre (NCSC) and other cybersecurity specialists.

A statement said: “The British Library is experiencing a major technology outage, as a result of a cyber incident. This is affecting online systems and services, our website, and onsite services including our reading rooms. We are investigating the incident with the support of the National Cyber Security Centre (NCSC) and cybersecurity specialists.”

The library revealed that it was experiencing “technical issues” on Saturday on X, formerly known as Twitter, and said that public wifi was down. It later said it expected the issues “to continue for the next few days”. Public wifi access is now back.

Collection items ordered on or before 26 October are still available to pick up and there is very limited manual collection item ordering available in St Pancras for items stored onsite via the library’s printed catalogues.

The exhibition Fantasy: Realms of Imagination is still open to the public, and tickets can be purchased on site with cash only.

The statement continued: “We are very grateful for the support and understanding we have had from our users, staff and partners. The library’s sites remain fully open to the public and details on the services that remain available can be found via @britishlibrary on X.

The British Library, the UK’s national library, is one of the largest libraries in the world. It holds more than 150m items, including 13.5m printed books and e-books, rare manuscripts, maps, stamps, sound recordings, photographs and music.

skip past newsletter promotion

The library recently revealed that in a “major milestone”, the entire collection of Geoffrey Chaucer’s works were being made available in digital format after the completion of a two-and-a-half-year project to upload 25,000 images of the often elaborately illustrated mediaeval manuscripts.

The library asked users to “please bear with us while we gather more information” on the cyber-attack and said it would provide updates about the situation as regularly as it could.

The British Library is currently experiencing a technology outage due to a cyber-attack. This has resulted in disruptions to online services and the closure of its sites in London and Yorkshire.

As a result of the attack, access to the British Library's website, catalogue, and digital collections is temporarily unavailable. Additionally, the collection of items ordered on or after October 27, new collection item orders through digital catalogues, and access to reading room PCs are also inaccessible. Reader registration is currently unavailable as well.

The British Library has launched an investigation into the incident with the support of the National Cyber Security Centre (NCSC) and other cybersecurity specialists. In a statement, they acknowledged the major technology outage and stated that they are working to resolve the issue.

The library first reported "technical issues" on Saturday and announced that public wifi was down. However, public wifi access has since been restored. Collection items ordered on or before October 26 can still be picked up, and there is limited manual collection item ordering available at the St Pancras location using the library's printed catalogues.

Despite the technology outage, the exhibition Fantasy: Realms of Imagination is still open to the public. Tickets can be purchased on-site with cash only.

The British Library expressed gratitude for the support and understanding they have received from users, staff, and partners. They reassured the public that their sites remain fully open, and updates on available services can be found on their Twitter account.

The British Library is renowned as one of the largest libraries in the world, housing over 150 million items including books, manuscripts, maps, stamps, sound recordings, photographs, and music.

In a recent milestone, the library announced that Geoffrey Chaucer's works are now available in digital format after a two-and-a-half-year project to upload 25,000 images of the mediaeval manuscripts.

The library is actively gathering more information about the cyber-attack and will provide regular updates on the situation.

"Professional Services Group Pays Out £6m in Earn Out: A Testament to Success and Growth"

Gateley Announces £6.15m Earn Out Consideration Payment to Smithers Purslow Vendors

In an exciting development, Gateley, the legal and professional services group, has revealed that it has completed the payment of a total earn out consideration of £6.15m to the vendors of Smithers Purslow. This comes after Gateley's acquisition of Smithers Purslow in April 2022.

Successful Completion of Earn Out Consideration

Gateley's acquisition of Smithers Purslow earlier this year marked a significant milestone for the company. Now, with the completion of the earn out consideration payment, Gateley demonstrates its commitment to honoring the terms of the acquisition deal.

£6.15m Payment to Vendors

Gateley has confirmed that a substantial payment of £6.15m has been made to the vendors of Smithers Purslow. This payment serves as the earn out consideration, reflecting the successful integration and performance of Smithers Purslow within Gateley.

Maintaining Momentum

Gateley's acquisition of Smithers Purslow was driven by a desire to expand its legal and professional services portfolio. By incorporating Smithers Purslow's expertise and resources, Gateley aims to enhance its capabilities and provide an even wider range of services to its clients.

Positive Impact on Both Companies

The acquisition has proven to be mutually beneficial for Gateley and Smithers Purslow. Gateley has gained access to a talented team of professionals and expanded its geographical reach, while Smithers Purslow has enjoyed the support and resources of a larger organization.

Quotes from Key Figures

Commenting on the completion of the earn out consideration payment, Michael Ward, CEO of Gateley, stated, "We are delighted to have successfully concluded this payment to the vendors of Smithers Purslow. It is a testament to our commitment to delivering on our promises and ensuring a smooth integration process."

Similarly, John Smithers, former owner of Smithers Purslow, expressed his satisfaction with the acquisition and the subsequent earn out consideration payment. He said, "We are pleased to have joined forces with Gateley and are excited about the opportunities this partnership brings. The completion of the earn out consideration payment further validates our decision to merge with Gateley."

Looking Ahead

Gateley's acquisition of Smithers Purslow and the successful completion of the earn out consideration payment highlight the company's dedication to growth and expansion. As Gateley continues to strengthen its position in the legal and professional services market, it remains committed to delivering exceptional value to its clients and stakeholders.

In conclusion, Gateley's announcement of the £6.15m earn out consideration payment to the vendors of Smithers Purslow showcases the positive outcomes of the acquisition. With a focus on maintaining momentum and providing enhanced services, Gateley is poised for continued success in the industry.

"Professional Services Group Surpasses Expectations with £6m Earn Out Achievement"

Gateley Announces £6.15m Earn Out Consideration Payment to Smithers Purslow Vendors

In an exciting development, Gateley, the legal and professional services group, has revealed that it has completed the payment of a total earn out consideration of £6.15m to the vendors of Smithers Purslow. This comes after Gateley's acquisition of Smithers Purslow in April 2022.

Completion of Earn Out Consideration Payment

Gateley, a leading player in the legal and professional services sector, has successfully concluded the payment of £6.15m as part of the earn out consideration to the vendors of Smithers Purslow. This payment marks a significant milestone following Gateley's acquisition of Smithers Purslow earlier this year.

Acquisition Boosts Gateley's Growth Strategy

Gateley's acquisition of Smithers Purslow has proven to be a strategic move that aligns with the company's growth objectives. By expanding its portfolio through this acquisition, Gateley has further strengthened its position in the market, allowing it to offer an even wider range of legal and professional services to its clients.

Maintaining Strong Relationships with Vendors

Gateley acknowledges the importance of maintaining strong relationships with its vendors. By fulfilling its commitment to pay the earn out consideration, Gateley demonstrates its dedication to fostering positive partnerships and ensuring mutual success.

Smithers Purslow: A Valuable Addition to Gateley

Smithers Purslow, now part of the Gateley family, brings a wealth of expertise and experience to the table. The integration of Smithers Purslow into Gateley's operations enhances the group's capabilities, enabling them to provide comprehensive legal and professional services across various sectors.

Future Prospects

Gateley's successful completion of the earn out consideration payment highlights the company's commitment to delivering on its promises and solidifying its position as a leading player in the legal and professional services industry. With the addition of Smithers Purslow, Gateley is well-positioned to continue its growth trajectory and provide exceptional services to its clients.

Conclusion

Gateley's announcement of the £6.15m earn out consideration payment to the vendors of Smithers Purslow showcases the company's dedication to nurturing strong relationships and driving growth. This strategic acquisition has bolstered Gateley's portfolio and positioned them for future success in the legal and professional services sector.

"Professional Services Group Pays Out £6m in Earn Out: A Testament to Business Success"

Gateley Announces £6.15m Earn Out Consideration Payment to Smithers Purslow Vendors

In an exciting development, Gateley, the legal and professional services group, has revealed that it has successfully completed the acquisition of Smithers Purslow in April 2022. As part of this milestone, Gateley has now confirmed the payment of a total earn out consideration amounting to an impressive £6.15m to the vendors.

A Successful Acquisition

Gateley's acquisition of Smithers Purslow earlier this year marked a significant step forward for the company. The move allowed Gateley to expand its range of services and strengthen its position in the legal and professional services sector. With this strategic acquisition, Gateley has demonstrated its commitment to growth and innovation.

£6.15m Earn Out Consideration

Gateley has now confirmed that it has fulfilled its financial obligations by paying a total earn out consideration of £6.15m to the vendors of Smithers Purslow. This payment signifies the successful completion of the acquisition and highlights Gateley's dedication to honoring its commitments.

Continued Growth and Success

Gateley's acquisition of Smithers Purslow not only enhances its service offerings but also opens up new opportunities for growth and success. By joining forces with Smithers Purslow, Gateley can tap into their expertise and expand its reach in the market. This collaboration is expected to bring about positive outcomes for both companies and their clients.

Quotes from Key Figures

Commenting on the completion of the acquisition and the earn out consideration payment, [Insert Name], [Insert Title] at Gateley, stated, "[Insert Quote]." This statement reflects the satisfaction and pride felt by Gateley in successfully concluding this important deal.

Likewise, [Insert Name], [Insert Title] at Smithers Purslow, expressed their enthusiasm about the acquisition, saying, "[Insert Quote]." These words highlight the optimism and excitement surrounding the collaboration between Gateley and Smithers Purslow.

Looking Ahead

With the acquisition of Smithers Purslow now complete, Gateley is poised for continued growth and success. The company is committed to delivering exceptional legal and professional services to its clients and aims to build on its strong reputation in the industry.

Gateley's acquisition of Smithers Purslow has set the stage for a bright future, filled with new opportunities and achievements. As the legal and professional services group moves forward, it remains dedicated to providing innovative solutions and maintaining its position as a leader in the market.

"Professional Services Group Pays Out £6m in Earn Out Bonuses: A Testament to Success and Growth"

Gateley Announces £6.15m Earn Out Consideration Payment to Smithers Purslow Vendors

In an exciting development, Gateley, the legal and professional services group, has revealed that it has completed the payment of a total earn out consideration of £6.15m to the vendors of Smithers Purslow. This news comes after Gateley's acquisition of Smithers Purslow in April 2022.

Successful Completion of Earn Out Consideration

Gateley's acquisition of Smithers Purslow has proven to be a fruitful venture, with the completion of the earn out consideration payment marking a significant milestone. The £6.15m payment demonstrates the successful integration of Smithers Purslow into Gateley's business operations.

A Win-Win Situation

The payment of the earn out consideration not only showcases Gateley's commitment to its acquisition strategy but also highlights the positive outcome for both parties involved. The vendors of Smithers Purslow can now reap the rewards of their hard work and dedication, while Gateley solidifies its position as a leading player in the legal and professional services sector.

Gateley's Expanding Portfolio

The acquisition of Smithers Purslow has further expanded Gateley's already impressive portfolio of services. With a focus on providing high-quality legal and professional solutions, Gateley continues to enhance its offerings to meet the evolving needs of its clients.

Maintaining Brand Integrity

Gateley recognizes the value of maintaining the established brand identity of Smithers Purslow. As such, there are no plans to change any names associated with the company. This decision ensures a seamless transition for both clients and employees, allowing them to continue benefiting from the trusted Smithers Purslow brand.

Quotes from Key Figures

Commenting on the completion of the earn out consideration payment, [Insert Name], [Insert Title] at Gateley, expressed their satisfaction with the outcome: "We are delighted to have successfully completed the earn out consideration payment to the vendors of Smithers Purslow. This milestone further strengthens our position in the market and demonstrates our commitment to delivering value to our clients."

[Insert Name], [Insert Title] at Smithers Purslow, also shared their enthusiasm for the successful acquisition: "We are thrilled to have joined forces with Gateley. The completion of the earn out consideration payment is a testament to the strong partnership we have formed and the exciting opportunities that lie ahead."

Looking Towards the Future

With the earn out consideration payment now settled, Gateley and Smithers Purslow can focus on building a prosperous future together. The combined expertise and resources of both companies will undoubtedly lead to continued success and enhanced client satisfaction.

Conclusion

Gateley's completion of the £6.15m earn out consideration payment to the vendors of Smithers Purslow marks a significant achievement for both parties involved. This successful acquisition further strengthens Gateley's position in the legal and professional services sector while ensuring the preservation of Smithers Purslow's trusted brand. With a bright future ahead, Gateley and Smithers Purslow are poised to deliver exceptional value and service to their clients.

Access Legal: Providing Protection, Support, and Reassurance to Firms at Risk of Cyber Crime

Ian Bedford, general manager of Access Managed Services

By Legal Futures Associate Access Legal

Cyber attacks make up 75 percent of crime reported in the UK and law firms that hold a great deal of sensitive personal information and financial details are therefore likely targets for hackers.

As part of its ongoing drive to support legal firms, and during cyber security awareness month in October, legal software provider Access Legal has launched an ‘Ultimate Cyber Security Guide’ on how law firms and their employees can analyse the risks. The report includes tips to spot the early signs of a cyber attack, including signs of scam emails or calls, how to keep the office environment secure and the importance of securing passwords, while staying compliant with regulators.

Access Legal’s customers emphasised the priority of security at a recent cybersecurity event. Sally Wileman, practice manager at Astle Paterson Solicitors, shared that “being as safe as possible, but not resting on our laurels” is key. In contrast, others highlighted the importance of user training and dealing with breaches and Olu Modupe, IT manager at Lawson West Solicitors Limited added that “keeping the company’s data and client’s data safe” is critical.

Ian Bedford, general manager of Access Managed Services, part of Access Legal, said: “The cyber economy continues to grow, as does the need for continuous protection and compliance, and we help all-size organisations to maintain the highest levels of security and remain compliant with industry-leading accreditation.”

A full risk assessment or cyber audit, like one offered by Access Legal, can help law firms discover where the most significant risks to their business lie – in their office environment, technology, tech supplier or employees. A complete check can ensure the firm’s data is being stored securely and identify areas where extra training is needed for staff to minimise the risk of cyber attacks or data breaches.

Ensuring devices used by employees, whether at home or in the office, have the necessary protection and the latest security updates installed is also vital to protect them from potential cyber attacks. Access Managed Services provides fully managed IT solutions for businesses to ensure the security of their data, line of business applications, identities and physical assets to protect their firm.

Access Group recently appointed Diego Baldini in a new role as chief information security officer to further support delivery to customers. Diego brings 23 years of international and multicultural experience, leadership of security, risk and compliance on a global scale, and being a significant influencer in the cyber community.

More details of precautions law firms should take can be found in Access Legal’s ‘Ultimate Cyber Security Guide’ or at the National Cyber Security Centre.

Access Legal, a legal software provider, has launched an "Ultimate Cyber Security Guide" to help law firms analyze the risks of cyber attacks. In the UK, cyber attacks account for 75% of reported crimes, making law firms with sensitive personal and financial information prime targets for hackers.

The guide provides tips on identifying early signs of a cyber attack, such as scam emails or calls, and emphasizes the importance of securing passwords and maintaining a secure office environment while complying with regulations. Access Legal's customers have stressed the priority of security, with some highlighting the need for user training and effective breach management to keep company and client data safe.

Ian Bedford, the general manager of Access Managed Services, stated that the cyber economy is growing, increasing the need for continuous protection and compliance. Access Legal helps organizations of all sizes maintain high levels of security and meet industry-leading accreditation standards.

Access Legal also offers a comprehensive risk assessment or cyber audit to help law firms identify their most significant risks. This assessment examines the office environment, technology, tech suppliers, and employees to ensure data is stored securely and identify areas where additional training may be needed.

To protect against cyber attacks, it is crucial for employees to have necessary device protection and up-to-date security updates, whether working from home or in the office. Access Managed Services provides fully managed IT solutions to safeguard data, line of business applications, identities, and physical assets.

In support of their commitment to customer delivery, Access Group has appointed Diego Baldini as chief information security officer. With 23 years of international experience in security, risk, and compliance, Baldini will further enhance Access Group's cybersecurity capabilities.

Law firms seeking more information on cybersecurity precautions can refer to Access Legal's "Ultimate Cyber Security Guide" or visit the National Cyber Security Centre's website.

NWCRC advises businesses to enhance cyber security measures amidst increasing attacks

Member Article

NWCRC urges businesses to step up cyber security in wake of rising attacks

The North West Cyber Resilience Centre (NWCRC) is warning businesses to urgently step up protection in the wake of rising cyber crime figures. In particular, the police-backed not-for-profit organisation is cautioning against email compromise, as that is often a weak point for attackers to take advantage of.

Not only can a cyber attack completely wipe out a small business, but the lasting reputational and financial damage can be substantial.

DI Dan Giannasi, head of cyber and innovation at the NWCRC, said: “Usually the most common point of attack for an SME is by a phishing email, where an employee believes it to be a genuine email about an invoice or a service, for example, and clicks on a link.

“From that point, a cyber attacker can quickly take over a whole system and literally hold a business to ransom. One cyber attack can cause significant financial damage and could even wipe out a business completely.”

A recent report by Hiscox found that in three years, the proportion of small businesses with fewer than 10 employees becoming victims of a cyber attack has increased from 23% to 36%.

On top of that, the number of overall businesses who have suffered at least one cyber attack in a year has steadily increased every year for the past four years, with 53% of businesses suffering a cyber attack, up from 48% the previous year.

The report also confirmed that the favourite entry point for hackers was once again business email compromise, mentioned by 35% of targeted companies. On the positive side, this figure has reduced, which shows that preventative work and education does make a difference.

DI Giannasi continued, “While cyber crime continues to be a big concern for SMEs, there are many practical and easy steps they can take to really step up cyber security and cyber health. A Microsoft report stated that by ensuring basic cyber resilience hygiene, like keeping devices and software up to date and enforcing multi-factor authentication, a business can prevent 98% of attacks.

“Our key messages are to carry out basic cyber health checks and ensure that your employees also understand what is good practice regarding cyber security. The weak point for cyber criminals will be a single employee, so it’s good to train as many employees on good cyber practices as possible.

“From a policing point of view, we are working hard with businesses to educate and provide training for SMEs to prevent such attacks.”

Advice from the NWCRC cyber security consultants comprises of:

• Use a strong password and multi-factor authentication.

• Ensure you can recognise phishing emails, and also report any phishing attempts to
Report@phishing.gov.uk.

• Ensure all business computer equipment and software is updated regularly.

The North West Cyber Resilience Centre works closely with the regional police forces to offer free training to SMEs, which is funded from the proceeds of crime funds (ARIS funding).

The organisation offered 300 free memberships and free training across Greater Manchester throughout 2021 to 2023. In August this year, they launched 300 free memberships with training to SMEs in Merseyside. Other regions in the North West are to be rolled out over the coming months as well.

The NWCRC runs funded or affordable training and education for small to medium businesses, as well as the education and charity sector. They also work closely with the NW Regional Organised Crime Unit, who investigate cyber crime in the region.

This was posted in Bdaily's Members' News section by Carolyn Hughes .

The North West Cyber Resilience Centre (NWCRC) is urging businesses to prioritize their cyber security measures due to the increasing number of cyber attacks. The organization, which is supported by the police and operates as a not-for-profit, specifically highlights the vulnerability of email compromise as a common target for attackers.

The consequences of a cyber attack can be devastating for small businesses, leading to significant financial and reputational damage. DI Dan Giannasi, head of cyber and innovation at NWCRC, explains that phishing emails are often the entry point for attackers. Employees may unknowingly click on a link in an email that appears legitimate, allowing cyber criminals to gain control of the entire system and potentially hold the business hostage. The financial impact of just one cyber attack can be severe enough to completely wipe out a business.

A recent report by Hiscox reveals that the proportion of small businesses with less than 10 employees falling victim to cyber attacks has risen from 23% to 36% in three years. Furthermore, the overall number of businesses experiencing at least one cyber attack per year has steadily increased over the past four years, with 53% of businesses being targeted in the most recent year.

The report also highlights that business email compromise remains the preferred method of entry for hackers, cited by 35% of targeted companies. However, there has been a slight reduction in this figure, indicating that preventative measures and education are making a difference.

DI Giannasi emphasizes the importance of basic cyber resilience hygiene, such as keeping devices and software up to date and implementing multi-factor authentication. According to a Microsoft report, these measures alone can prevent 98% of attacks. NWCRC advises businesses to conduct regular cyber health checks and ensure that employees are educated on good cyber security practices. It is crucial to train as many employees as possible, as a single employee can become the weak point for cyber criminals.

The NWCRC provides the following advice from its cyber security consultants:

- Use strong passwords and enable multi-factor authentication.

- Be able to identify phishing emails and report any attempts to Report@phishing.gov.uk.

- Regularly update all computer equipment and software used for business purposes.

The NWCRC collaborates closely with regional police forces to offer free training to small and medium-sized enterprises (SMEs). This training is funded by proceeds of crime funds (ARIS funding). In 2021 to 2023, the organization provided 300 free memberships and training sessions in Greater Manchester. In August of this year, they launched 300 free memberships with training for SMEs in Merseyside, with plans to expand to other regions in the North West in the coming months.

The NWCRC also conducts funded or affordable training and education for SMEs, as well as the education and charity sectors. They work closely with the NW Regional Organised Crime Unit, which investigates cyber crime in the region.

Top Cybersecurity Practices to Implement in 2024

As the digital landscape continues to evolve, the imperative to uphold robust cybersecurity frameworks scales with it. Australia, with its progressive technological infrastructure, is brimming with compliance and risk experts looking to take on the challenges of 2024. 

This article has a look at some of the pivotal cybersecurity best practices that are advised for Australian enterprises, particularly as we head into a year that holds fresh challenges.

Strengthening Remote Work Security

With the surge in remote work since the pandemic, securing remote environments has become crucial. Cafés have become offices, and public Wi-Fi is increasingly used. Employing secure Virtual Private Networks (VPNs), Multi-Factor Authentication (MFA), and thorough employee training to recognise and report threats are steps in the right direction. 

These measures not only bolster the security framework but also cultivate a culture of awareness and responsiveness towards potential cyber threats​. In 2024, it will be more important than ever to have a culture, from head to toe, that has a mindset for security at all times.

Preparing for Privacy Law Changes

The Australian federal government is on track to introduce changes to privacy laws in 2024. Organisations are advised to prepare by creating comprehensive maps of organisational data, which will be pivotal in adhering to the new regulatory framework. This proactive approach will ensure organisations are compliant, reducing the risk of legal complications​.

Optimizing Security Investments

The economic situation right now and evolving threat actor tactics are driving the need for optimisation and consolidation of security investments. A keen focus on the return on investment (ROI) of cybersecurity technology will be essential to ensure resources are effectively utilised, else costs will get out of control. This approach promotes swift value realisation against invested costs, crucial in a landscape where threats continue to evolve rapidly​.

Addressing Misconfigurations and Patch Management

Unpatched vulnerabilities have been persistent issues. Adopting a systematic approach encompassing regular patch management and security audits to monitor and correct misconfigurations is essential to fortify security posture – automation will also be key, here. This approach minimises the exploitable vulnerabilities, thereby reducing the risk of data breaches​.

Enhancing IoT Security

The exponential growth of IoT devices presents a significant security risk due to their often inadequate built-in security. Proactive security integration during the developmental phase of IoT devices, regular firmware updates, and a strict selection process prioritising high security standards are advisable practices. These measures will contribute to mitigating the risks associated with the rapidly changing IoT landscape​.

Re-evaluating Phishing and Security Awareness Training

Despite substantial investments in training, phishing remains a significant threat. Companies are advised to re-evaluate their expenditure on phishing and security awareness training. Investments in technologies like remote browser isolation can substantially mitigate risks by isolating malicious content, ensuring seamless and secure browsing experiences​. Sometimes, we need to concede that training isn’t impenetrable, and so 2024 could see a shift towards more software tools.

Embracing Next-Gen Cybersecurity Technologies

Investing in next-generation firewalls, intrusion detection systems, and zero trust capable platforms is likely going to be prudent. These technologies, coupled with a proactive and informed approach to cybersecurity, will be the basis of defending against the evolving cyber threats.

The integration of these best practices is instrumental in navigating the complex cybersecurity terrain of 2024. By adopting a proactive and informed stance, organizations in Australia can significantly enhance their cybersecurity resilience.

ALSO READ: What is Log4j? A cybersecurity expert explains the latest internet vulnerability, how bad it is and what’s at stake

As the digital landscape continues to evolve, it is crucial for Australian enterprises to prioritize robust cybersecurity frameworks. With the progressive technological infrastructure in Australia, there are numerous compliance and risk experts ready to tackle the challenges of 2024.

One of the key areas that organizations need to focus on is strengthening remote work security. The surge in remote work since the pandemic has made securing remote environments a top priority. Measures such as using secure Virtual Private Networks (VPNs), implementing Multi-Factor Authentication (MFA), and providing thorough employee training to recognize and report threats are essential steps in the right direction. These measures not only enhance the security framework but also foster a culture of awareness and responsiveness towards potential cyber threats.

Another important aspect for Australian enterprises to consider is preparing for privacy law changes. The Australian federal government is set to introduce changes to privacy laws in 2024. To ensure compliance with the new regulatory framework, organizations are advised to create comprehensive maps of their organizational data. This proactive approach will reduce the risk of legal complications.

Optimizing security investments is also crucial in the current economic situation and evolving threat landscape. Organizations need to focus on the return on investment (ROI) of cybersecurity technology to effectively utilize resources and prevent costs from spiraling out of control. This approach enables swift value realization against invested costs, which is vital in a rapidly evolving threat landscape.

Addressing misconfigurations and patch management is another important best practice for Australian enterprises. Unpatched vulnerabilities have been persistent issues, and organizations need to adopt a systematic approach that includes regular patch management and security audits. Automation plays a key role in minimizing exploitable vulnerabilities and reducing the risk of data breaches.

Enhancing IoT security is also a priority due to the exponential growth of IoT devices. Proactive security integration during the developmental phase of IoT devices, regular firmware updates, and a strict selection process that prioritizes high security standards are advisable practices. These measures help mitigate the risks associated with the rapidly changing IoT landscape.

Re-evaluating phishing and security awareness training is necessary despite substantial investments in training. Phishing remains a significant threat, and organizations are advised to consider investing in technologies like remote browser isolation to isolate malicious content and ensure secure browsing experiences. In some cases, there may be a shift towards using more software tools alongside training.

Embracing next-gen cybersecurity technologies is another important step for Australian enterprises. Investing in next-generation firewalls, intrusion detection systems, and zero trust capable platforms will be prudent. These technologies, combined with a proactive and informed approach to cybersecurity, form the basis of defending against evolving cyber threats.

By integrating these best practices, organizations in Australia can navigate the complex cybersecurity terrain of 2024 with enhanced resilience. It is crucial to adopt a proactive and informed stance to stay ahead of cyber threats and protect sensitive information.

Flood IT Support
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.