"Davies and Sabio Forge Dynamic Partnership to Revolutionize Contact Centre Operations"
Davies Partners with Sabio Group to Revolutionize Contact Centre Technology
Professional services firm, Davies, has recently announced its partnership with digital customer experience specialist, Sabio Group. This collaboration aims to bring about a significant transformation in Davies' contact centre technology and infrastructure. With this strategic move, Davies is set to enhance its customer service capabilities and deliver an exceptional experience to its clients.
Improving Customer Experience through Technology
Davies recognizes the importance of providing top-notch customer service in today's competitive business landscape. By teaming up with Sabio Group, a renowned expert in digital customer experience, Davies aims to leverage cutting-edge technology to enhance its contact centre operations. This collaboration will enable Davies to deliver seamless and personalized customer experiences, ultimately improving overall customer satisfaction.
Transforming Contact Centre Technology
The partnership between Davies and Sabio Group will focus on revolutionizing the firm's contact centre technology and infrastructure. By implementing advanced solutions and innovative tools, Davies aims to streamline its operations and optimize its customer support processes. This transformation will enable Davies to handle customer inquiries more efficiently, reducing wait times and enhancing the overall customer journey.
Embracing Innovation for Success
In today's digital age, businesses must embrace innovation to stay ahead of the curve. Davies understands this necessity and has chosen Sabio Group as its trusted partner for this transformative journey. Sabio Group's expertise in digital customer experience will empower Davies to leverage the latest technologies and industry best practices. By adopting innovative solutions, Davies is poised to achieve operational excellence and deliver exceptional customer service.
Looking Towards a Bright Future
With the collaboration between Davies and Sabio Group underway, both organizations are excited about the positive impact it will have on their operations. By combining their strengths, they aim to create a contact centre that is not only efficient but also customer-centric. This partnership reflects Davies' commitment to continuously improving its services and ensuring client satisfaction.
Conclusion
Davies' decision to partner with Sabio Group marks a significant step towards transforming its contact centre technology and infrastructure. By embracing innovation and leveraging cutting-edge solutions, Davies is set to revolutionize its customer service capabilities. This collaboration highlights Davies' dedication to providing exceptional customer experiences and staying at the forefront of the industry. As this partnership unfolds, both Davies and Sabio Group are eager to witness the positive outcomes it will bring to their organizations.
Learn How Microsoft 365 Copilot Is Going to Transform M365 Apps
Advanced AI is a new buzzword in cloud computing. The launch of tools like ChatGPT and Bard have made big waves. Developers are now racing to introduce the next level of features to apps. Features that do part of your work for you. Such as writing emails or making follow-up checklists based on contact data.
These AI-based applications do much more than automate processes. People are using them to write business correspondence, create websites, and write scripts. AI is also quickly transforming the everyday office workflow.
Microsoft is one of the biggest players in the office application field. It’s at the forefront of introducing transformative technology. The company is about to transform Microsoft 365 in a huge way with its new Copilot tool.
Microsoft 365 Copilot is a new tool designed to help users get the most out of their Microsoft 365 apps. This revolutionary tool is an intelligent, personalized assistant. It's designed to help users navigate and use M365 more efficiently.
In this article, we'll take a closer look at Microsoft 365 Copilot. And tell you the key ways it's going to improve M365 apps and your business workflows.
What is Microsoft 365 Copilot?
Microsoft 365 Copilot is an AI-powered assistant. It helps users with their day-to-day tasks in M365 apps. It's like having a personal assistant right in your Office apps. Users can ask questions, get help with tasks, and receive personalized recommendations. Copilot responds leveraging the context of their usage patterns.
Microsoft 365 Copilot works across all M365 apps. This includes:
Word
Excel
PowerPoint
Outlook
Teams
and more
Whether you're doing any number of tasks, Microsoft 365 Copilot is there to assist you. This includes working on a document, meeting scheduling, or collaborating with a team.
How Does Microsoft 365 Copilot Work?
Microsoft 365 Copilot uses AI and machine learning to understand users' needs. It provides personalized help. It uses data from users' interactions with M365 apps. It learns a user's usage patterns and offers recommendations based on their preferences.
For example, say you frequently use certain features in Excel. Microsoft 365 Copilot will learn this. It will offer suggestions when it detects that you're working on a similar task.
Say that you're working on a presentation in PowerPoint and struggling with design. Microsoft 365 Copilot can offer design suggestions based on your company's brand guidelines.
Microsoft 365 Copilot can also help users with common tasks. Tasks such as, scheduling meetings and managing emails. Users can simply ask Copilot for help. They can ask it to schedule a meeting or find an email from a specific person, and Copilot will take care of the rest.
Why is Microsoft Copilot Important?
Copilot is important because it can help users be more productive and efficient. By providing personalized support, the tool can save users time and reduce frustration.
Imagine you're working on a report in Word and you're struggling to format a table. Instead of spending time searching for a solution online. Or trying to figure it out on your own, you can simply ask Microsoft 365 Copilot for help. Copilot can offer suggestions. It can even walk you through the process, saving you time and reducing frustration.
Microsoft 365 Copilot is also important because it can help users get more out of their M365 apps. Many users may not be aware of all the features and capabilities of their M365 apps. But with Copilot, they can discover new ways to work more efficiently and effectively.
The capabilities of Copilot go even further. Say that you need to give your team an update on a marketing strategy. You won’t need to dig out emails, chat threads, or meeting notes. Instead, you can ask Copilot to “tell my team how we updated the marketing strategy.” The app will then search all those places for you and craft an update for your team.
Need a first draft of a meeting agenda or presentation? Just ask Copilot. It can access existing M365 documents and content and craft an initial draft for you.
Benefits of Using Microsoft 365 Copilot
Personalized Help
Microsoft 365 Copilot provides personalized help based on users' usage patterns and preferences. This means that users get the help they need when they need it, without having to search for solutions on their own.
Time-Saving
Microsoft 365 Copilot can help users save time on common tasks. Such as scheduling meetings and formatting documents. It can take on many information gathering tasks, like summarizing meeting notes. This saves users considerable time. Especially for manual tasks such as searching for information.
Knowledge workers spend an average of 2.5 hours per day searching for information.
Reduced Frustration
Microsoft 365 Copilot can help reduce frustration. It provides solutions when users are stuck on a task. The tool can also help users struggling with an Excel chart or table. Instead of having to figure out how to generate it, they can simply give a command to Copilot to do it for them.
Improved Productivity
Microsoft Copilot handles tasks that go beyond what business apps have historically done. For example, you can use it in PowerPoint to create a presentation for you. Use a command such as, “Create a six-slide presentation based on (this) document.” You can also tell it to find appropriate Microsoft stock photos and insert them.
The sky is the limit right now for how much this tool is going to impact office productivity.
When Will Microsoft 365 Copilot Be Available?
At the writing of this article, Microsoft hasn’t announced a release date yet. It is currently testing Copilot with a limited number of users. You will most likely see it coming out sometime soon.
Improve Your Microsoft 365 Value & Security
Need help with security or setup in Microsoft 365? Give us a call today to talk to one of our cloud app experts.
Understanding the Consequences of Human Error on Cyber Security
In this episode of The Indian Express weekly tech podcast – Our Own Devices, host Nandagopal Rajan is joined by Anshuman Sharma, Associate Director CSIRT & Investigative Response, APJ, Verizon Business to discuss the human factor in cybersecurity, exploring how human errors can significantly weaken cybersecurity measures and the various ways to safeguard against bad actors.
Edited by Abhishek Kumar
——
Introducing Anshuman Sharma (00:00) Human error in cyber security (00:51) Social engineering (01:32) Error in misconfiguration (04:41) Privilege misuse (07:18) Ensuring cyber hygiene (08:18) Customized training (09:56) Threat actors leveraging AI (13:14) Explaining operational technology (OT) (14:34) Difficulties in training workforce (15:18) Using AI to ensure cyber security (18:13)
More info
More less
The impact of human error on cyber securityIn this episode of The Indian Express weekly tech podcast – Our Own Devices, host Nandagopal Rajan is joined by Anshuman Sharma, Associate Director CSIRT & Investigative Response, APJ, Verizon Business to discuss the human factor in cybersecurity, exploring how human errors can significantly weaken cybersecurity measures and the various ways to safeguard against bad actors. Edited by Abhishek Kumar ------ Introducing Anshuman Sharma (00:00)
Human error in cyber security (00:51)
Social engineering (01:32)
Error in misconfiguration (04:41)
Privilege misuse (07:18)
Ensuring cyber hygiene (08:18)
Customized training (09:56)
Threat actors leveraging AI (13:14)
Explaining operational technology (OT) (14:34)
Difficulties in training workforce (15:18)
Using AI to ensure cyber security (18:13)
In this episode of The Indian Express weekly tech podcast - Our Own Devices, host Nandagopal Rajan is joined by Anshuman Sharma, Associate Director CSIRT & Investigative Response, APJ, Verizon Business. They discuss the impact of human error on cybersecurity and explore how these errors can weaken cybersecurity measures. They also provide various ways to safeguard against bad actors.
The conversation covers several important topics. Anshuman Sharma introduces himself at the beginning of the episode. He then delves into the concept of human error in cybersecurity, explaining how it can pose a significant threat. Social engineering is also discussed, highlighting how attackers manipulate individuals to gain unauthorized access to systems.
Misconfiguration errors are another area of concern. Sharma explains how mistakes in system configuration can lead to vulnerabilities that can be exploited by cybercriminals. Privilege misuse, where individuals abuse their authorized access to systems, is also addressed.
To ensure strong cybersecurity, Sharma emphasizes the importance of maintaining cyber hygiene. This involves implementing best practices and regularly updating security measures. Customized training programs are also recommended to educate employees about potential threats and how to mitigate them.
The conversation then shifts to the use of artificial intelligence (AI) by threat actors. Sharma explains how AI can be leveraged by cybercriminals to enhance their attacks and why it is crucial for organizations to stay updated on these advancements.
Operational technology (OT) is another topic covered in the discussion. Sharma provides an explanation of OT and its significance in the context of cybersecurity.
The difficulties in training the workforce to effectively combat cyber threats are also acknowledged. Sharma discusses the challenges organizations face in keeping their employees well-informed and prepared to tackle evolving cybersecurity risks.
Finally, the conversation concludes with a discussion on using AI to ensure cybersecurity. Sharma highlights the potential of AI in strengthening security measures and emphasizes the need for organizations to adopt AI-driven solutions.
Overall, this episode provides valuable insights into the human factor in cybersecurity and offers practical strategies to safeguard against cyber threats.
Understanding the consequences of human error on cyber security
In this episode of The Indian Express weekly tech podcast – Our Own Devices, host Nandagopal Rajan is joined by Anshuman Sharma, Associate Director CSIRT & Investigative Response, APJ, Verizon Business to discuss the human factor in cybersecurity, exploring how human errors can significantly weaken cybersecurity measures and the various ways to safeguard against bad actors.
Edited by Abhishek Kumar
——
Introducing Anshuman Sharma (00:00) Human error in cyber security (00:51) Social engineering (01:32) Error in misconfiguration (04:41) Privilege misuse (07:18) Ensuring cyber hygiene (08:18) Customized training (09:56) Threat actors leveraging AI (13:14) Explaining operational technology (OT) (14:34) Difficulties in training workforce (15:18) Using AI to ensure cyber security (18:13)
More info
More less
The impact of human error on cyber securityIn this episode of The Indian Express weekly tech podcast – Our Own Devices, host Nandagopal Rajan is joined by Anshuman Sharma, Associate Director CSIRT & Investigative Response, APJ, Verizon Business to discuss the human factor in cybersecurity, exploring how human errors can significantly weaken cybersecurity measures and the various ways to safeguard against bad actors. Edited by Abhishek Kumar ------ Introducing Anshuman Sharma (00:00)
Human error in cyber security (00:51)
Social engineering (01:32)
Error in misconfiguration (04:41)
Privilege misuse (07:18)
Ensuring cyber hygiene (08:18)
Customized training (09:56)
Threat actors leveraging AI (13:14)
Explaining operational technology (OT) (14:34)
Difficulties in training workforce (15:18)
Using AI to ensure cyber security (18:13)
In this episode of The Indian Express weekly tech podcast - Our Own Devices, Nandagopal Rajan is joined by Anshuman Sharma, Associate Director CSIRT & Investigative Response, APJ, Verizon Business, to discuss the impact of human error on cybersecurity. They explore how human errors can weaken cybersecurity measures and discuss various ways to safeguard against bad actors.
The conversation covers several important topics related to cybersecurity. Anshuman Sharma introduces himself at the beginning of the episode. He then delves into the issue of human error in cybersecurity, highlighting its significance and potential consequences.
Social engineering is another topic discussed in the podcast. The hosts explain how attackers exploit human vulnerabilities to gain unauthorized access to systems and data. They emphasize the need for awareness and vigilance to prevent falling victim to social engineering attacks.
Misconfiguration errors are also addressed in the conversation. The hosts discuss how simple mistakes in configuring systems can lead to security vulnerabilities. They stress the importance of proper configuration practices to mitigate these risks.
The podcast moves on to discuss privilege misuse, where individuals with authorized access abuse their privileges for malicious purposes. The hosts emphasize the need for strict access controls and monitoring to prevent such misuse.
Ensuring cyber hygiene is highlighted as a crucial aspect of maintaining strong cybersecurity. The hosts discuss best practices for maintaining good cyber hygiene, such as regularly updating software, using strong passwords, and implementing multi-factor authentication.
Customized training is also mentioned as an effective way to enhance cybersecurity awareness and skills among employees. The hosts discuss the importance of tailored training programs that address specific organizational needs and challenges.
The conversation then shifts to the topic of threat actors leveraging artificial intelligence (AI) for cyber attacks. The hosts explain how AI can be used by attackers to automate and enhance their malicious activities. They emphasize the need for organizations to stay updated on AI advancements and develop countermeasures accordingly.
Operational technology (OT) is explained as a critical component of many industries, including manufacturing and infrastructure. The hosts discuss the unique cybersecurity challenges associated with OT systems and the need for specialized training and expertise in securing them.
The podcast concludes with a discussion on the difficulties organizations face in training their workforce on cybersecurity. The hosts highlight the need for continuous training and education to keep up with evolving threats and technologies.
Lastly, the hosts touch upon the use of AI in ensuring cybersecurity. They discuss how AI can be leveraged to detect and respond to threats in real-time, enhancing overall security measures.
Overall, this episode provides valuable insights into the human factor in cybersecurity and offers practical advice on safeguarding against cyber threats.
"The Crucial Role of Brand Foundations in Driving Success for Professional Services Firms"
Title: Don Scales, Global CEO of Investis Digital, Reflects on the Evolution of the Business World
Introduction:
Don Scales, the esteemed Global CEO of Investis Digital and co-author of the book "How to Lead a Values-Based Professional Services Firm," takes us on a journey back in time to a pivotal moment in the business world. Let's delve into how this event transformed the landscape and shaped the industry we know today.
The Game-Changing Event:
Eighteen years ago, the business world was shaken to its core by an event that would forever alter its trajectory. This momentous occasion left an indelible mark on the industry, prompting significant changes and inspiring professionals like Don Scales to adapt and thrive.
Don Scales: A Visionary Leader:
Don Scales, a prominent figure in the business realm, has witnessed firsthand the transformative power of this event. As the Global CEO of Investis Digital, he has successfully navigated the ever-changing landscape, leading his firm to new heights. Scales' expertise and insights have made him a sought-after thought leader in the industry.
The Evolution of Business:
In the aftermath of this game-changing event, the business world underwent a remarkable evolution. Traditional practices were challenged, and new approaches emerged. Companies began to prioritize values and ethics, recognizing their impact on long-term success.
Embracing Values-Based Leadership:
Don Scales, along with his co-author, has explored the concept of values-based leadership in their book. This approach emphasizes the importance of aligning business strategies with core values, fostering a positive work culture, and building strong relationships with clients and employees alike.
The Ripple Effect:
The impact of this event rippled across industries, forcing professionals to reevaluate their practices and adapt to a rapidly changing environment. Companies that embraced innovation and adopted values-based leadership thrived, while those resistant to change struggled to keep up.
Quotes from Don Scales:
Reflecting on this transformative period, Don Scales shared his insights, stating, "The business world was forever altered, and it became clear that values-based leadership was no longer a luxury but a necessity for success." He further emphasized the importance of building trust and maintaining transparency in business relationships.
Looking Ahead:
As we move forward, the lessons learned from this event continue to shape the business world. Professionals like Don Scales remain committed to leading with integrity, embracing innovation, and fostering a culture of collaboration. The future holds exciting possibilities as businesses adapt and thrive in an ever-evolving landscape.
Conclusion:
Don Scales, the Global CEO of Investis Digital, offers us a glimpse into the transformative event that shook the business world eighteen years ago. Through his leadership and commitment to values-based practices, Scales has successfully navigated the evolving industry. As we look ahead, we can draw inspiration from his insights and embrace the opportunities that lie before us.
"The Crucial Role of Brand Foundations in Driving Success for Professional Services Firms"
Title: Don Scales, Global CEO of Investis Digital, Shares Insights on Leading a Values-Based Professional Services Firm
Introduction:
Don Scales, the Global CEO of Investis Digital and co-author of the book "How to Lead a Values-Based Professional Services Firm," has been making waves in the business world for nearly two decades. With a focus on ethical leadership and fostering a values-driven culture, Scales has been instrumental in transforming the way professional services firms operate.
The Rise of Values-Based Leadership:
In the past, the business world was shaken by a groundbreaking shift towards values-based leadership. Don Scales played a pivotal role in this transformation, advocating for a more ethical approach to running professional services firms. Recognizing that profit should not be the sole driving force behind business decisions, Scales championed the integration of values and purpose into corporate strategies.
Embracing Ethical Practices:
Scales firmly believes that businesses should prioritize ethical practices to build trust and credibility. By aligning their actions with their stated values, companies can create a positive impact on both their employees and the wider community. Scales emphasizes the importance of transparency, integrity, and accountability in all aspects of business operations.
Creating a Values-Driven Culture:
One of Scales' key contributions has been his emphasis on fostering a values-driven culture within professional services firms. He believes that when employees are aligned with the company's core values, they are more engaged, motivated, and committed to delivering exceptional results. By creating an environment that encourages open communication and collaboration, Scales has successfully cultivated a culture where employees feel valued and empowered.
The Power of Purpose:
Scales understands that purpose is a driving force behind success. He encourages leaders to define and communicate a clear purpose that resonates with both employees and clients. By articulating a compelling vision, companies can attract top talent, inspire innovation, and differentiate themselves in the market.
Quotes from Don Scales:
- "Values-based leadership is not just a trend; it is a fundamental shift in how businesses should operate. By prioritizing ethics and purpose, we can create a more sustainable and impactful future."
- "Building a values-driven culture requires continuous effort and commitment from leaders. It starts with setting the right example and empowering employees to make decisions aligned with our shared values."
- "Purpose gives us direction and fuels our passion. It is the driving force behind our success and the reason why we do what we do."
Conclusion:
Don Scales, the Global CEO of Investis Digital, has been at the forefront of the values-based leadership movement for nearly two decades. Through his advocacy for ethical practices, fostering a values-driven culture, and embracing purpose, Scales has transformed the way professional services firms operate. His insights serve as a guiding light for leaders aspiring to create positive change and make a lasting impact in their organizations.
"The Crucial Role of Brand Foundations in Driving Success for Professional Services Firms"
Title: Don Scales, Global CEO of Investis Digital, Shares Insights on Leading a Values-Based Professional Services Firm
Introduction:
Don Scales, the Global CEO of Investis Digital and co-author of the book "How to Lead a Values-Based Professional Services Firm," has been making waves in the business world for nearly two decades. With a focus on ethical leadership and fostering a values-driven work environment, Scales has become a prominent figure in the industry.
Embracing Ethical Leadership:
Scales firmly believes in the power of ethical leadership and its impact on professional services firms. He emphasizes the importance of aligning company values with client needs, ensuring transparency, and building trust. By prioritizing ethics, businesses can create a positive work culture that attracts top talent and fosters long-term success.
The Paradigm Shift:
Eighteen years ago, the business world experienced a significant shift when ethical considerations began to take center stage. Companies were forced to reevaluate their practices and adapt to a new era of transparency and accountability. Scales played a crucial role during this transformative period, advocating for values-based leadership and helping organizations navigate these changes.
The Book: "How to Lead a Values-Based Professional Services Firm":
Scales' expertise and insights are now encapsulated in his co-authored book, "How to Lead a Values-Based Professional Services Firm." This comprehensive guide offers practical advice for leaders looking to build a values-driven organization. It explores topics such as defining core values, aligning them with business strategies, and fostering an ethical work environment.
The Importance of Values in Professional Services:
According to Scales, values play a pivotal role in professional services firms. By establishing clear values, companies can differentiate themselves from competitors and attract clients who share similar principles. Additionally, values provide a foundation for decision-making, ensuring that businesses uphold their ethical standards even in challenging situations.
Quotes from Don Scales:
Scales emphasizes the significance of values, stating, "Values are the guiding principles that shape an organization's culture and define its identity. They are the compass that steers us in the right direction, even when faced with difficult choices." He also highlights the impact of ethical leadership, saying, "Ethical leaders inspire trust, foster collaboration, and create a positive work environment where employees can thrive."
Conclusion:
Don Scales, the Global CEO of Investis Digital, continues to be a leading voice in the business world. With his focus on ethical leadership and values-based professional services, he has helped shape the industry's landscape. Through his book and ongoing efforts, Scales aims to empower leaders to build organizations that prioritize ethics, transparency, and long-term success.
The potential risks faced by CISA's security-by-design initiative and a proposed way forward
The Biden administration’s 2023 National Cybersecurity Strategy identified structural shortcomings in the state of cybersecurity, calling out the failure of market forces to adequately distribute responsibility for the security of data and digital systems. Most prominently, the strategy seeks to “rebalance responsibility [for security] to those best positioned.”
Shortly after the strategy’s launch in March of this year, the Cybersecurity and Infrastructure Security Agency (CISA) kicked off an effort to “shift the balance of cybersecurity risk” by pushing firms to adopt security-by-design (SbD) practices, improving the safety and security of their products at the design phase and throughout their life cycle.
CISA director Jen Easterly’s announcement of these efforts appears to put CISA at the forefront of this rebalancing, addressing technology vendors’ incentives to underinvest in security through changes in how those firms design and deploy the products they sell. As the first substantive proposal from President Biden’s administration to effectuate this rebalancing since the launch of the strategy, the success or failure of the SbD initiative could be a bellwether for one of the strategy’s two fundamental ideas.
Success with SbD is at risk, however, both from the political challenges of implementing SbD practices and the threat of unrealistic expectations. This piece addresses both and highlights a path forward.
Political and structural headwinds
The politics of SbD implementation — which implicitly require a capacity to compel change in vendor practices, as well as the insight to design them — are treacherous ground for CISA, as the fast-growing agency is not a regulator. In time, it might become one, but current and past leadership insist that such responsibilities would be at odds with agency culture and its operational responsibilities.
The agency’s ability to support, build capacity, train, coordinate, and plan together with state, local, tribal and territorial entities, and industry stakeholders is rooted in its disposition as a trusted partner and neutral convener.
This means CISA should be only one of several federal agencies working to implement SbD, with cooperation from regulators like the Federal Trade Commission (FTC), a sharp and pointy complement to CISA’s open-handed approach. Otherwise, the SbD initiative could place CISA in a bind, trying to fix entrenched market incentive problems but without the ability to compel companies to act differently. CISA efforts to create accountability might undermine its attempts to generate goodwill.
Developing and defining a set of SbD practices that vendors can attest to, and that the U.S. government and other parties can verify or enforce, is a tremendous undertaking in and of itself. CISA must build SbD practices alongside an architecture for enforcement that sets clear roles for entities like the FTC, the Department of Defense, the Securities and Exchange Commission, and the General Services Administration.
The White House has responsibility here, too, and specifically the Office of the National Cyber Director, to guide this multi-agency effort within a strategy to manage the industry politics of shifting the incentives in this market — precisely what the office was designed, staffed, and organized to do. CISA’s focus must remain on enumerating and updating the essential SbD practices.
Just one piece of the puzzle
As we have argued before, “no strategy can address all sources of risk at once, but . . . silver bullets often trade rhetorical clarity for crippling internal compromises.” The SbD program could achieve deep, meaningful changes in how some of the largest technology vendors build services and products. Those changes would have material benefits for the security of every technology user.
However, cajoling all firms toward a comprehensive and uniform set of best practices is a fundamentally incompletable task.
Malicious actors perpetually seek new means of exploit; different sectors and system classes face different and unique challenges; and new technologies are prone to modes of failure, both new and unforeseen. Adopting certain new processes, rigorously enforcing them, and fixing existing incentives would still be a much-needed improvement over the current status quo.
However, adopting memory-safe languages or pushing large actors toward better risk management would not necessarily have prevented many significant vulnerabilities in recent memory, such as Log4Shell. To succeed, CISA will also need to understand how large technology companies build products and services — current industry practice is far from complete or perfect, but it is the baseline from which SbD hopes to drive change. Understanding that baseline is critical.
There is danger when rhetoric around shifting responsibility in cyberspace suggests that cybersecurity problems and challenges exist only because technology vendors cut corners or that all cybersecurity risk can be avoided by following a simple set of straightforward practices. The increasingly interconnected, dependent nature of software systems, as well as the variety of organizations and systems they connect to, creates risks all its own.
SbD is an important piece of managing this — the status quo of responsibility deferred to the user is broken — but describing SbD as a panacea risks creating backlash when insecurity inevitably persists.
It is clear CISA recognizes that success in SbD could be one of the most impactful policy interventions in cybersecurity in the last decade. It is also clear that the program, even in its most successful incarnation, will leave some problems unsolved. Specificity about the scope and goals of the program will help prevent its inevitable critics from distorting the debate into all-or-nothing terms.
Risk and opportunity
SbD — the first policy manifestation of the National Cybersecurity Strategy’s effort to shift responsibility — will not come about by sheer goodwill alone. CISA is not a regulator, and it must define a path for federal agencies that are regulators so that the implementation of SbD leverages the broader standards setting, enforcement, and regulatory powers of the federal government.
Shying away from direct government enforcement of these security practices risks consigning the effort to history, alongside many other “voluntary” and “industry-led” programs.
The growing and talented team at CISA have 18 months until January 2025, which will bring either the paralyzing tumult of transition or the still-chaotic maturation of a first-term administration into a second. The largest vendors that would participate in this program are not going anywhere and can afford to wait.
In this sense, CISA and the wider U.S. government’s cyber policy apparatus is on the clock. CISA must focus on the essential elements of SbD and organize, build, and engage with a clear deadline in mind. The clock is ticking.
The Biden administration's 2023 National Cybersecurity Strategy has identified flaws in the current state of cybersecurity, particularly the lack of responsibility for data and digital system security. The strategy aims to redistribute responsibility to those best equipped to handle it. In line with this strategy, the Cybersecurity and Infrastructure Security Agency (CISA) has launched an initiative to promote security-by-design (SbD) practices among firms. This initiative seeks to improve the safety and security of products from the design phase to their entire life cycle.
CISA director Jen Easterly's announcement of this initiative positions CISA as a leader in rebalancing cybersecurity incentives for technology vendors. By changing how these firms design and deploy their products, CISA aims to address the problem of underinvestment in security. The success or failure of the SbD initiative will serve as a test for the effectiveness of the overall strategy.
However, there are political and structural challenges that could hinder the implementation of SbD practices. CISA is not a regulator, and its ability to enforce change in vendor practices is limited. Cooperation with regulatory agencies like the Federal Trade Commission (FTC) is crucial to ensure effective implementation. Additionally, developing a set of SbD practices and establishing an enforcement architecture is a complex task that requires collaboration among multiple agencies.
It is important to note that SbD is just one piece of the puzzle in addressing cybersecurity risks. While it can bring significant improvements, it cannot eliminate all vulnerabilities. Malicious actors constantly find new ways to exploit systems, and different sectors face unique challenges. Understanding the current industry practices is essential for driving meaningful change through SbD.
Describing SbD as a panacea for cybersecurity risks can create unrealistic expectations and backlash when vulnerabilities persist. It is crucial to be specific about the scope and goals of the program to prevent distortion in the debate.
Implementing SbD will require more than goodwill. CISA must define a path for regulatory agencies to leverage their enforcement powers. Shying away from government enforcement risks rendering the effort ineffective, similar to previous voluntary and industry-led programs.
CISA and the wider U.S. government's cyber policy apparatus have a limited timeframe to make progress. The clock is ticking, and CISA must prioritize essential elements of SbD and work towards a clear deadline.
"Breaking: Latest Developments in the World of Professional Services"
Showcase Your Company News and Gain Guaranteed Exposure in Print and Online
Introducing Outstanding Women in Business: Leaders Driving Change, Earning Admiration, Inspiring the Community, and Delivering Results
In today's fast-paced business world, it is crucial to recognize the exceptional women who are making a significant impact. These outstanding women are not only driving change within their industries but also earning admiration, inspiring their communities, and consistently delivering remarkable results. Now, you have the opportunity to showcase your company's news alongside these remarkable women and gain guaranteed exposure both in print and online.
Highlighting the Achievements of Exceptional Women
Our Outstanding Women in Business feature aims to celebrate the achievements of extraordinary women who are breaking barriers and shattering glass ceilings. By participating in this exclusive opportunity, you can shine a spotlight on your company's accomplishments while aligning yourself with these trailblazing individuals.
Guaranteed Exposure in Print and Online
When you choose to showcase your company news through our Outstanding Women in Business feature, you can be confident that your story will reach a wide audience. Your news will be prominently featured both in our print publication and on our highly-trafficked website, ensuring maximum visibility among our readership.
Inspire and Motivate Others
By sharing your company's news alongside stories of exceptional women, you have the power to inspire and motivate others. Your achievements can serve as a catalyst for change, encouraging aspiring professionals to pursue their dreams fearlessly and reminding them that anything is possible.
How to Participate
Participating in our Outstanding Women in Business feature is simple. Just submit your company news, highlighting any recent accomplishments or milestones, along with a brief description of how your organization is driving positive change. Our dedicated team of journalists will review your submission and craft a compelling article that showcases your news alongside the stories of other outstanding women.
Don't Miss Out on This Exclusive Opportunity
Don't miss the chance to gain guaranteed exposure for your company's news and align yourself with the exceptional women who are shaping the business landscape. Showcase your achievements, inspire others, and make a lasting impact by participating in our Outstanding Women in Business feature. Contact us today to submit your company news and secure your spot in this highly anticipated publication.
Remember, the deadline for submissions is fast approaching, so act now to ensure your story is included in this prestigious showcase of outstanding women in business.
SEC adopts cyber-security rules without including director expertise component
The SEC on Wednesday voted three-to-two to approve rules requiring companies to disclose material cyber-security incidents that affect them. They will also have to report each year material information about their cyber-security risk management, strategy and governance – although the commission has dropped a controversial proposal that companies report on board-level cyber-security expertise.
Under the new rules, firms will have to report on a new Item 1.05 of Form 8K any cyber-security incident they believe to be material and to describe the material aspects of its nature, scope and timing, in addition to its material impact – or reasonably likely material impact – on the company.
In most cases such reports will be due four business days after the company decides that an incident is material. The company will be able to delay making the disclosure if the US Attorney General determines that revealing the incident would pose a substantial risk to national security or public safety.
The new rules also add Item 106 to Regulation SK. This will require companies to describe in their Form 10K the board’s oversight of cyber-security risks and management’s role and expertise in assessing and managing material cyber-security risks. They will also have to describe their processes for assessing, identifying and managing material risks from cyber-security threats and the material impact of cyber-security risks.
The Form 8K disclosures will be due beginning the later of 90 days after the rule is published in the Federal Register or December 18, 2023. The Form 10K disclosures will be due beginning with annual reports for fiscal years ending on or after December 15, 2023.
Board experts?
The SEC initially proposed adding Item 407(j) to require disclosures about the cyber-security expertise, if any, of a company’s board members. The measure attracted a lot of feedback and was ultimately dropped.
The agency writes in the final rule: ‘After considering the comments, we are not adopting proposed Item 407(j). We are persuaded that effective cyber-security processes are designed and administered largely at the management level, and that directors with broad-based skills in risk management and strategy often effectively oversee management’s efforts without specific subject matter expertise, as they do with other sophisticated technical matters.’
There are different schools of thought about the need for specific board expertise to address topics such as cyber-security, artificial intelligence, climate change and human capital management. Many governance professionals favor directors having more general expertise and focusing on their role of risk oversight.
The National Association of Corporate Directors (NACD) welcomed the rule changes overall, saying in a statement that a more formalized disclosure on cyber-security risk management, strategy, governance and incident disclosure will ‘create efficiencies and clarity around cyber-risk oversight expectations.’
NACD also welcomed the SEC’s decision to drop the board expertise requirement. The group had written in its comment letter to the agency: ‘The presence of a cyber-security expert on a board cannot make up for poor oversight processes and does not excuse the full board from its oversight duties in this matter.’ It expressed approval that the final rule ‘focuses disclosure of expertise at the correct tier of responsibility for mitigating this risk: management.’
Divided commission
The changes have – as in many cases in recent years – divided opinion among the commissioners. SEC chair Gary Gensler said in a statement: ‘Whether a company loses a factory in a fire — or millions of files in a cyber-security incident — it may be material to investors. Currently, many public companies provide cyber-security disclosure to investors. I think companies and investors alike, however, would benefit if this disclosure were made in a more consistent, comparable and decision-useful way.
‘Through helping to ensure that companies disclose material cyber-security information, today’s rules will benefit investors, companies and the markets connecting them.’
Caroline Crenshaw, SEC
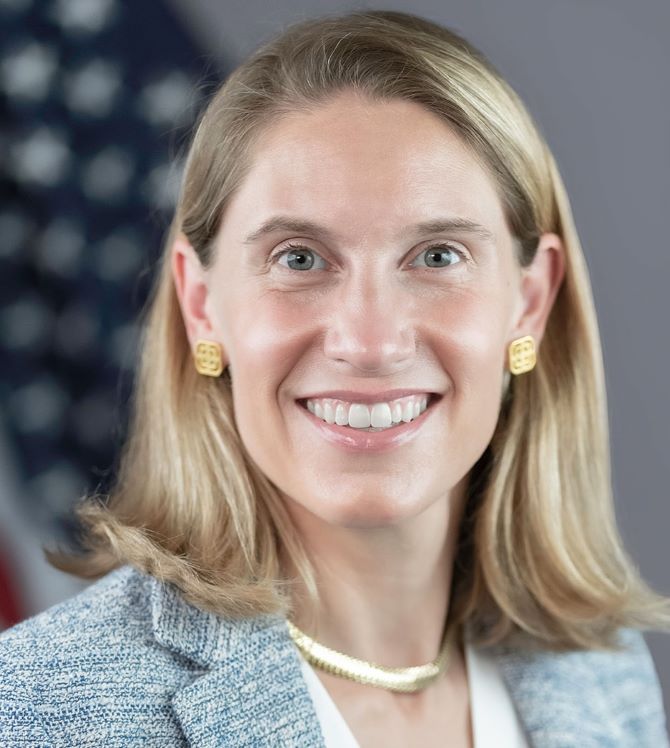
Commissioner Caroline Crenshaw, who voted in favor of the reforms, said: ‘[A]s the comment file substantiated, knowledge of cyber-security threats and breaches are essential to understanding a firm. Among other reasons, breaches can (and do) result in loss of revenue, customers and business opportunities. Those harms may be realized or they may be ongoing in the form of lost sensitive information, remediation costs and losses in shareholder value.
‘Despite the consensus on the harmful nature of cyber-incidences, commenters highlighted that existing disclosure practices vary in substance, organization and presentation, thus establishing a need for, and benefit of, comparable, reliable and decision-useful disclosures to investors.’
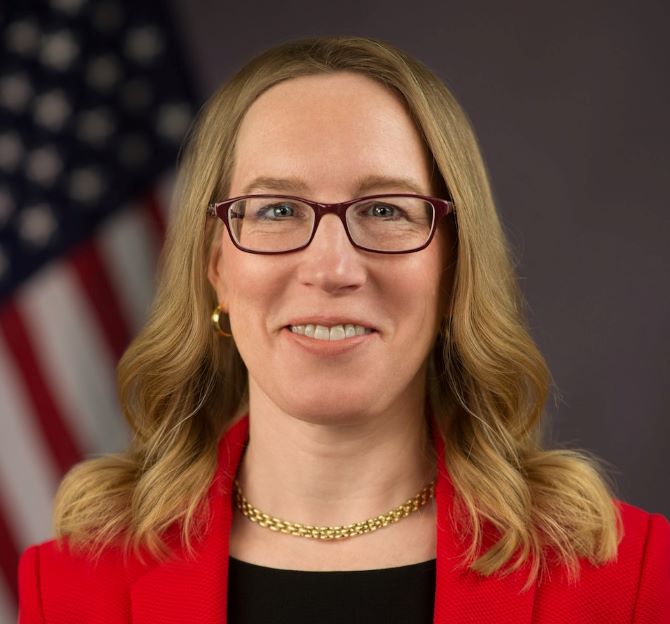
Hester Peirce, who voted against the changes, complained that they ignore the limits of the agency’s disclosure authority and investors’ best interests while not establishing why they are needed. ‘The release prescribes granular disclosures, which seem designed to better meet the needs of would-be hackers rather than investors’ need for financially material information,’ she said.
Caroline Crenshaw, SEC
‘The new rule, for example, requires disclosure of detailed information about issuers’ cyber risk management processes and governance and relevant personnel… The strategy and governance disclosures risk handing them a roadmap on which companies to target and how to attack them.’
She also commented: ‘[T]he SEC’s potentially non-material risk management and governance disclosures veer into managing companies’ cyber-defenses; the new rule looks like a compliance checklist for handling cyber risk, a checklist the SEC is not qualified to write.’
Despite approving of the changes overall, NACD also said it remains concerned that the four-day reporting window ‘may not allow companies the time to put in place adequate patches and protections before being forced to make it known that they have been compromised digitally.’
The Securities and Exchange Commission (SEC) has approved new rules that require companies to disclose material cyber-security incidents and provide annual reports on their cyber-security risk management, strategy, and governance. However, the controversial proposal to report on board-level cyber-security expertise has been dropped. Under the new rules, companies must report any material cyber-security incident on Form 8K and describe its nature, scope, timing, and impact. Reports are due within four business days of determining the incident is material, unless the US Attorney General determines that disclosure would pose a risk to national security or public safety. The rules also add Item 106 to Regulation SK, requiring companies to describe the board's oversight of cyber-security risks and management's role in assessing and managing such risks. The disclosures will be due starting December 18, 2023. The SEC decided not to adopt the proposed requirement for board members to have cyber-security expertise, stating that effective cyber-security processes are primarily managed at the management level. The National Association of Corporate Directors (NACD) supports the rule changes and believes that disclosure of expertise should focus on management rather than the board. The SEC's decision has divided opinion among the commissioners, with Chair Gary Gensler emphasizing the importance of consistent and comparable cyber-security disclosure for investors, while Commissioner Hester Peirce argues that the rules go beyond the agency's authority and may provide hackers with valuable information. NACD also expresses concern about the short reporting window for cyber-security incidents, as it may not allow companies enough time to address vulnerabilities before making them public.